 InfoSecBulletin Cybersecurity for mankind
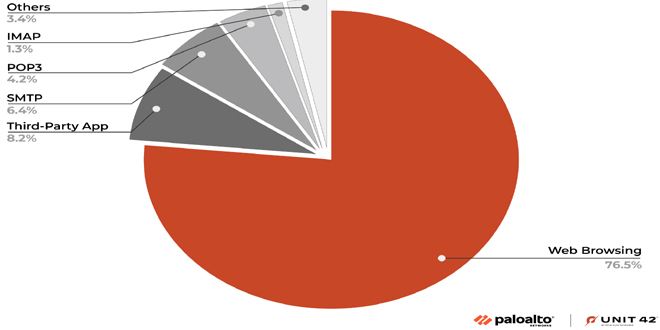
Threat actors are resorting to employing URLs to send ransomware, as they constantly search for innovative methods to deceive victims and bypass their defenses. They are employing more and more sophisticated tactics to distribute their ransomware is making their actions more dynamic. Threat actors often use different versions of ransomware and frequently change hostnames, paths, filenames, or a combination of these to distribute ransomware widely.
ALSO READ:
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

Unit 42 analyzed 7,000 random URLs out of 27,000 unique ones and found different techniques used by ransomware gangs to avoid detection, takedown, or blocking of malicious sites. To overcome victims’ defenses, threat actors have now resorted to utilizing URLs as the foremost method of distributing ransomware.
To see the full report of Unit 42 CLICK



