 InfoSecBulletin Cybersecurity for mankind

ShinyHunters has publicly claimed responsibility for the Ernst & Young (EY) data breach. The group posted a message on their dark web site. It says they will release all stolen data by July 31, 2026, unless EY talks to them before the mentioned date.
EY shared details about the incident earlier this month. They noticed strange activity on April 23, 2026, in an IT system used by their staff for tax client support.
Daily Cyber security update for 06.11. 2026
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

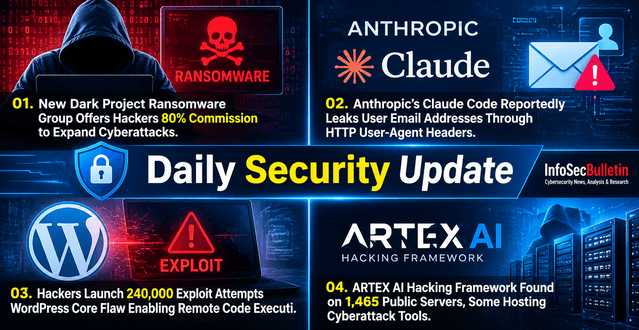
Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

An investigation showed that a unauthorized person got into the platform from March 28 to April 12, 2026, and downloaded documents from many EY clients.
EY sent letters to regulators like the Attorneys General of California and Texas to report a problem. They confirmed that at least 1,366 people in several US states are affected, but the number is likely much higher due to the firm’s worldwide clients.
ShinyHunters’ Extortion Claim
Until this week, no threat actor had claimed the attack, and EY had not disclosed how intruders breached the third-party platform. That changed when ShinyHunters listed EY on its leak site alongside other new victims, including RingCentral and Brinks Home, asserting the intrusion originated from a supply-chain attack that yielded credentials to EY’s internal systems.

EY Data Breach Claimed by ShinyHunters
The group’s leak-site notice, updated July 27, 2026, warns, “This is a final warning to reach out by 31 July 2026 before we leak along with several ongoing (digital) problems” if EY fails to respond to their contact attempts.
This plan is similar to what ShinyHunters has done before in their attacks on Instructure, Charter Communications, and McGraw Hill. They took advantage of SaaS platforms, SSO credentials, and vishing attacks to steal a lot of data and then asked for ransom.
ShinyHunters has become one of the biggest extortion groups in 2026. They run a special leak site and often take advantage of weak points in other companies instead of breaking into networks directly.
While puhlishing the report, EY has not confirmed ShinyHunters’ specific claims or responded publicly to the July 31 deadline, and no stolen data has yet appeared on underground forums.



