InfoSecBulletin Cybersecurity for mankind

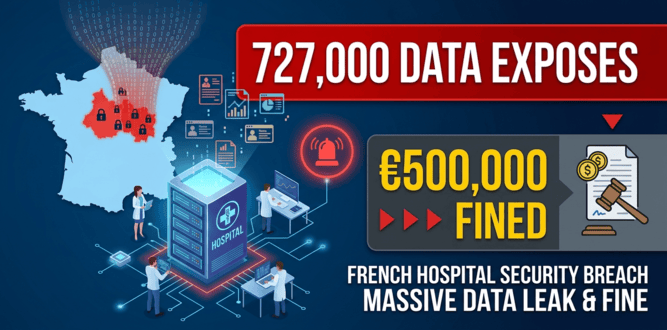
France’s data protection authority (CNIL) has fined Hôpital privé de la Loire €500,000 ($580,000) for not properly protecting the data of patients and their families. The French agency says that security problems caused a data leak in the summer of 2025. This exposed sensitive information about 524,867 patients and 202,246 other trusted people.
Hôpital privé de la Loire (HPL) is a general hospital in Saint-Étienne. It is part of the Ramsay Santé healthcare group. It offers medical, surgical, maternity, cancer, emergency, and intensive care services. The hospital has 650 workers, including 180 doctors. It has 333 beds in five departments and treats about 60,000 patients each year.
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Last year, a hacker access into the hospital’s electronic patient record system and took sensitive information from over 727,000 people who got care at HPL, took patients there, or helped them.
After the incident, the CNIL started an investigation. They found many issues with the hospital’s duty to follow the General Data Protection Regulation (GDPR).
Some of the shortcomings CNIL’s investigation identified include:
External users, including private-practice physicians, could access the system without a VPN or multi-factor authentication.
Inadequate access controls allowed the compromised account to access records for all hospital patients.
The hospital lacked real-time or near-real-time monitoring and alerting, allowing the attacker to explore the system and extract a large volume of data over several days without detection.
The hospital informed affected patients but did not directly notify the 202,246 trusted third parties whose data was also stolen.
The flaws mentioned are about Article 32 and Article 34 of the GDPR. The committee saw that HPL made some security upgrades while the process was ongoing.
A teenage hacker called “Marak” said he did it. He reached out to the French news site Le Progrès on Telegram and said the attack started with breaking into one doctor’s account. This gave access to HPL’s whole internal system.
The hacker tried to sell the stolen data to one buyer for €2,000 to €5,000, but later it was reported that the data was not sold or shared.
Related News:
French state services hit by ‘intense’ cyber attack
French National Bank Account Registry Exposes 1.2M Bank Accounts