InfoSecBulletin Cybersecurity for mankind

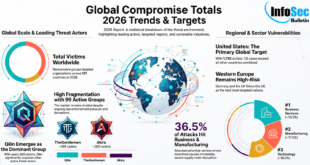
Global ransomware attacks stayed very high in the first seven months of 2026. There were 5,064 confirmed victims in 135 countries. This shows that money-driven cybercrime is still growing. Data from ransomware leak sites reveals that 111 active ransomware groups attacked businesses, government offices, hospitals, manufacturers, and important infrastructure worldwide.
United States Remains the Primary Target
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The United States still stands out in ransomware victim numbers, making up over a third of all known victims. In 2026, ransomware groups named more than 2,000 organizations in the U.S.
The countries most affected include:
| Rank | Country |
|---|---|
| 1 | United States |
| 2 | Germany |
| 3 | United Kingdom |
| 4 | Canada |
| 5 | Italy |
| 6 | France |
| 7 | Spain |
| 8 | Brazil |
| 9 | India |
| 10 | Australia |
Mexico, Thailand, Japan, Taiwan, and Turkey were also among the most targeted countries. The high number of attacks on rich countries shows that ransomware criminals focus on groups with more money and a better chance of paying ransoms.

Attack Volume Peaked in April
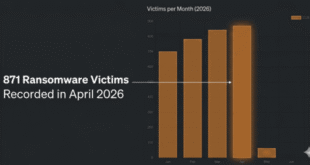
Victim counts showed a steady rise in the first quarter of the year and reached the highest point in April.
| Month | Victims |
|---|---|
| January | ~700 |
| February | ~780 |
| March | ~840 |
| April | ~865 |
| May | ~790 |
| June | ~705 |
| July* | ~360 |
***July reflects partial data.
Activity went down after April, but ransomware attacks stayed high, with over 700 victims each month on average as per ransomware.live.

Qilin Emerges as the Most Active Ransomware Group
Qilin has become the most active threat among the 111 ransomware groups being tracked in 2026.
Top 10 Ransomware Groups (2026)
| Rank | Group |
|---|---|
| 1 | Qilin |
| 2 | TheGentlemen |
| 3 | Akira |
| 4 | IncRansom |
| 5 | DragonForce |
| 6 | LockBit5 |
| 7 | NightSpire |
| 8 | Play |
| 9 | Clop |
| 10 | CoinBaseCartel |
Qilin had about 700 victims, staying well ahead of TheGentlemen and Akira. The ongoing presence of groups like Akira, Play, Clop, and LockBit5 shows that well-known ransomware operations are still very active, even with greater law enforcement actions.
Business Services Faces the Highest Risk
Ransomware groups keep attacking industries that can quickly lose money when things stop working.
The most targeted sectors include:
Business Services
Manufacturing
Technology
Healthcare
Consumer Services
Construction
Financial Services
Agriculture & Food Production
Transportation & Logistics
Public Sector
Business had the highest number of attacks, followed by Manufacturing and Technology companies. Healthcare and finance companies are good targets because they need to work all the time and their data is very important.
Key Findings
5,064 victims have already been recorded in 2026.
111 ransomware groups are actively operating.
Victims span 135 countries.
The United States remains the most targeted nation by a wide margin.
April 2026 recorded the highest monthly attack volume.
Qilin is the most active ransomware group this year.
Business Services, Manufacturing, and Technology remain the industries at greatest risk.
The 2026 ransomware situation shows that cybercriminal groups are still changing their methods even with police actions and more spending on defense. New ransomware brands are appearing next to old ones, showing the strength of the ransomware-as-a-service (RaaS) system.
By using multi-factor authentication, keeping offline backups, using endpoint detection and response (EDR) tools, constantly checking for signs of problems, and practicing response to incidents regularly organizations should make their cyber safety stronger. As ransomware groups focus more on important sectors and supply chains, taking action to improve security is key to reducing disruptions and money loss.