 InfoSecBulletin Cybersecurity for mankind
Cisco has said that a serious security flaw CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being used in attacks. The flaw has a highest CVSS score of 10.0. It lets remote attackers, who are not logged in, get around security checks and run scripts or commands as the admin on weak devices.
“In August 2026, the Cisco PSIRT became aware of active exploitation of this vulnerability,” Cisco updated its CVE-2026-20079 advisory to say on Wednesday. Cisco first mentioned CVE-2026-20079 in March. The company said it had no proof that anyone was using the flaw in attacks.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

The flaw happens because of a improper system process that starts when the device boots up. It can be taken advantage of by sending special HTTP requests to the device’s web interface.
The weakness impacts Cisco Secure FMC Software and Cisco Security Cloud Control Firewall Management. Cisco states it has already fixed the cloud-hosted Security Cloud Control service.
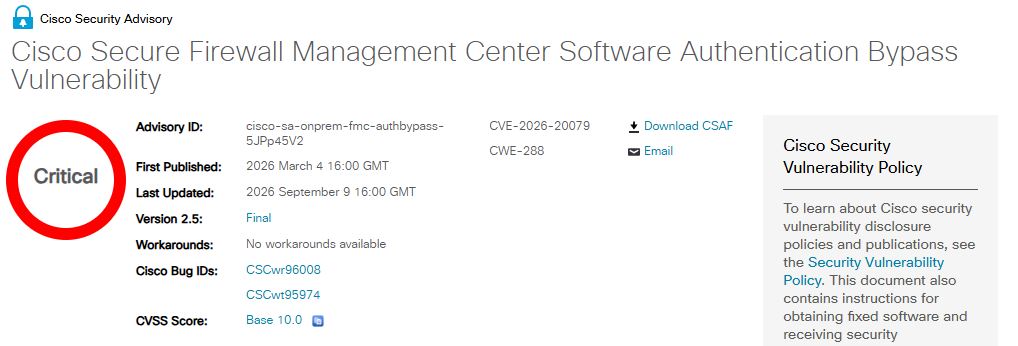
Cisco says there are no fixes and suggests that customers update to the newest software version.
Cisco advises customers who see signs of compromise to reach out to its TAC for help. They warn that installing the hot fixes will stop future attacks but won’t fix devices that are already affected.



