InfoSecBulletin Cybersecurity for mankind
In March, 807 ransomware victims were recorded as per ransomware.live. It is gradually increasing comparing to the previous two months. In 2026, 67 hacker groups are recorded to be active and Qilin is in the first with 356 victims.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

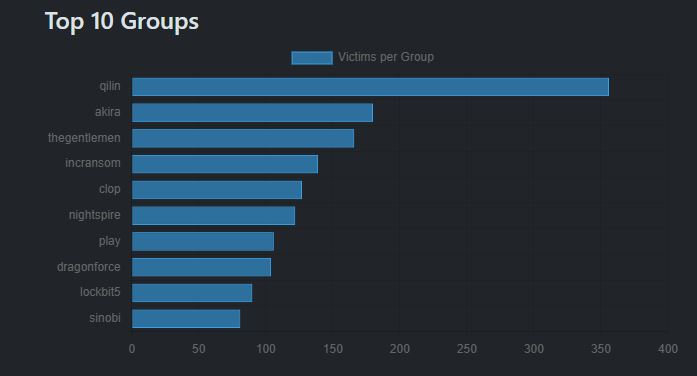
The chart shows the Top 10 Ransomware Groups based on how many attacks they have made (victims) in 2026. Qilin is in the lead with over 350 victims, almost twice as many as the next group, Akira, which has around 180 victims. The Gentlemen is in third place, while Incransom, Clop, and Nightspire are in the middle, each having between 120 and 150 victims.
The bottom part of the leaderboard shows Play and Dragonforce, both near 100 victims. They are followed by Lockbit5 and Sinobi, with Sinobi having about 80 victims. This information shows a strong threat where one group, Qilin, does a lot of global ransomware. However, having ten busy groups shows a varied and active crime scene.
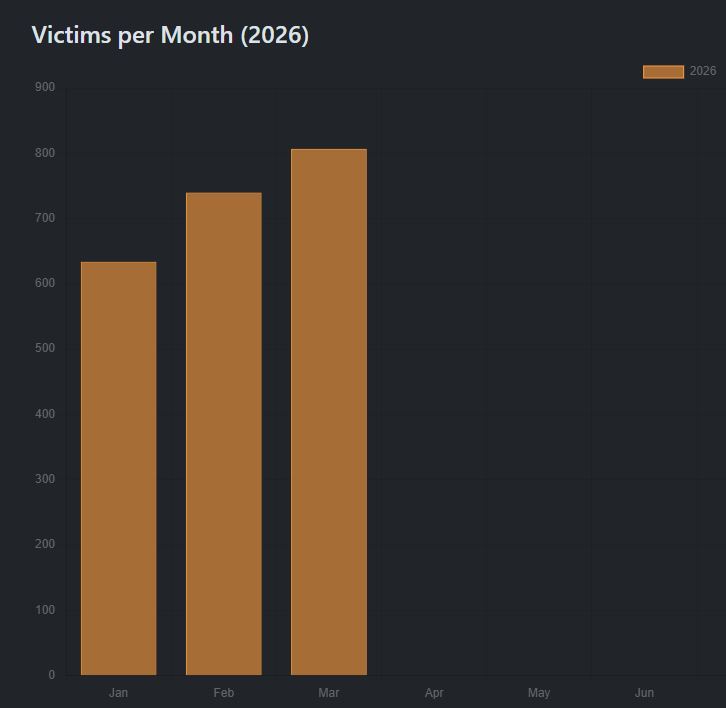
The chart shows a worrying rise in ransomware victims in the first part of 2026. The year started high in January with about 630 victims, but this number quickly grew to about 740 in February. In March, the number went even higher, reaching over 800 victims, the highest for the quarter. The data shows a steady increase in successful cyberattacks, with about a 27% jump from January to March.
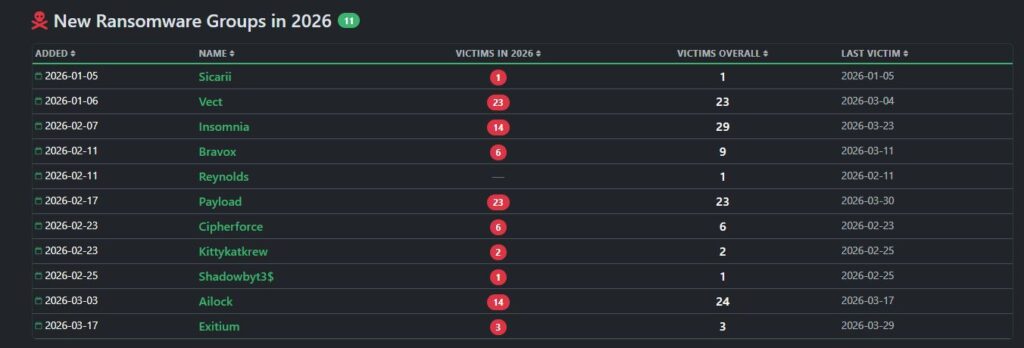
The table shows that 11 new ransomware groups appeared in the first quarter of 2026, showing a fast change in threats. Vect and Payload are the toughest, each taking 23 victims in 2026, and Payload was still active as of March 30. Other important new groups are Insomnia and Ailock, which quickly gathered 29 and 24 victims respectively, showing they work well soon after starting.
The data shows that many new groups came in February. Six new groups joined, like Bravox, Cipherforce, and a unique one called Kittykatkrew. Some groups, such as Sicarii and Shadowbyt3$, only affected one person each. However, new players keep appearing, like Exitium, which started in mid-March. This means the ransomware scene is always changing. The many new threat actors, some already targeting multiple victims, highlight how unpredictable and growing cybercrime is in 2026.
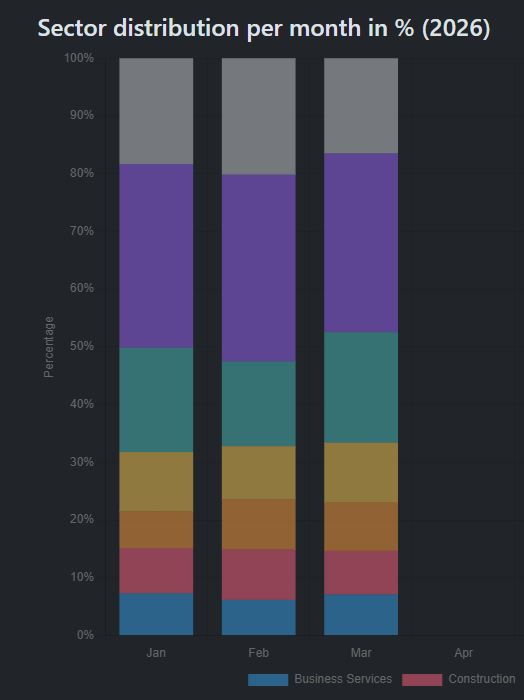
The number of ransomware victims in early 2026 follows a clear trend across different industries. In January, February, and March, the “Others” (purple) and Technology (light grey) sectors were hit the hardest, making up almost half of all attacks. The Manufacturing (teal) and Healthcare (gold) sectors also remained strong, with Manufacturing seeing a slight rise by the end of March. In contrast, sectors like Business Services, Construction, and Financial Services had smaller and steady shares, usually between 5% and 10%. Overall, while there were more victims during this time, the breakdown among these industries stayed steady, showing that attackers kept their focus on the global economy.