InfoSecBulletin Cybersecurity for mankind
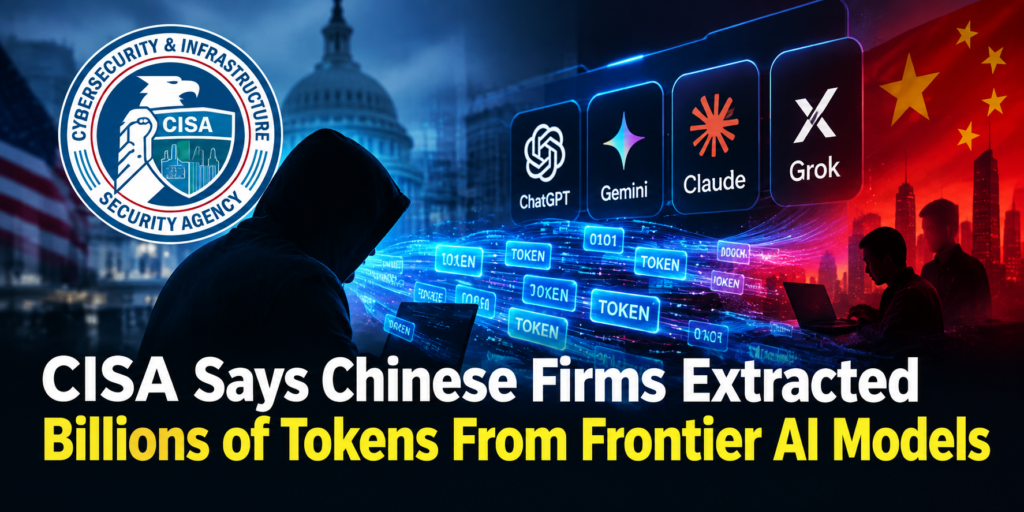
Six Chinese AI companies ran large-scale attacks on American AI models since late 2024, according to U.S. cybersecurity and intelligence agencies. A joint advisory from CISA, NSA, and the FBI states that DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI extracted billions of tokens through millions of requests from frontier AI models from Anthropic, OpenAI, Google, and xAI.
The agencies believe that the size and complexity of the operations show that the Chinese government knows about it. They say this method is probably a main part of the development plan for the companies involved.
Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

AI model distillation is a legitimate technique in which a “student” model learns from the outputs of a well-trained model, helping researchers and developers reduce training costs and speed up AI deployment.
Google warned in February that distillation attacks can happen outside the companies’ controlled areas. These attacks misuse API access to take knowledge and logic from strong models and compete with them for much less training cost.
CISA’s warning says that Chinese companies send API requests through fake or shared accounts, APIs, cloud services, aggregators, and “transfer station” proxies to get around location limits, usage caps, and detection. Some prompts tried to reveal limited reasoning, while automated systems changed providers and saw if defenders had lowered the responses.
“Advanced industrial-scale distillation tactics include chain-of-thought (CoT) reasoning extraction, automated failover between pathways during blocking attempts, and sophisticated quality evaluation frameworks to detect defensive countermeasures,” the advisory explains.
“China-based AI companies that conduct industrial-scale distillation against U.S. AI models see significantly shorter AI development timelines and reduced financial expenditures in training a frontier model.”
DeepSeek and MoonShot AI were the main companies that worked on creating simpler versions of multiple Claude, GPT, Gemini, and Grok models. MiniMax also followed behind, focusing on Claude, Gemini, and GPT models.
Alibaba and StepFun are said to be focusing on Claude and GPT models to make their products better, while Z.AI reportedly focused on GPT-5.5 and Claude Opus 4.8.
The advisory suggests that AI companies should enhance their ability to spot bad behavior and infrastructure issues. They should also change their actions if they think distillation activities are happening and share information about these actions with everyone involved.
Potential signs are new accounts quickly using the most allowed, constant activity without breaks, shared accounts from many IP addresses or devices, the same requests to different providers, very high subscription-to-usage ratios, and organized changes in how to access.