 InfoSecBulletin Cybersecurity for mankind
An unknown security expert called Nightmare Eclipse has drops a new Microsoft Defender flaw called “ShieldCrash” right after Microsoft released its security updates in September 2026. ShieldCrash is described as a bypass for the ShieldBreak Defender privilege escalation flaw patched on Thursday, which itself bypassed RoguePlanet, another Defender flaw disclosed in June and patched by Microsoft in July.
Nightmare Eclipse says that the ShieldCrash proof-of-concept exploit allows attackers to get SYSTEM privileges on updated Windows 10, Windows 11, and Windows Server systems, but they cannot write to those systems.
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

“Microsoft has failed to properly patch ShieldBreak CVE-2026-69414, under specific conditions it is still possible to trigger the exact same problem that was caused by ShieldBreak. While Microsoft fixed several things to prevent re-exploiting the issue, they missed a spot where ShieldBreak can still be exploited,” they said.
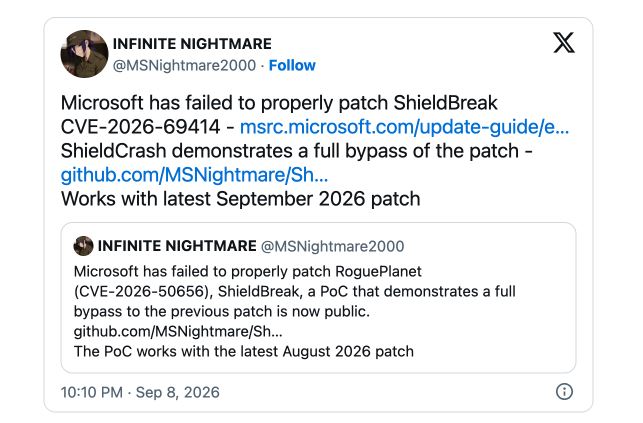
“This PoC demonstrates an arbitrary file read as SYSTEM with September 2026, all supported windows versions are affected. I might rework this later into a full SYSTEM PoC but for now I’m dropping this skeleton PoC because I’m feeling a bit lazy.”
Nightmare Eclipse shared these zero-day exploits as part of a fight with Microsoft about the company’s bug bounty and how they handle reporting vulnerabilities.
Microsoft responded with warnings of legal action against anyone engaging in “malicious activity causing real harm” to its customers, prompting many to believe that the company was directly threatening the security researcher.
Since April, a secret security researcher has revealed many zero-day problems. These include ShieldBreak, LegacyHive, RoguePlanet, BlueHammer, RedSun, YellowKey, GreenPlasma, MiniPlasma, and UnDefend. They target Microsoft Defender, BitLocker, and other Windows parts.
Microsoft fixed the ShieldBreak, RoguePlanet, YellowKey, GreenPlasma, and MiniPlasma issues, but there is still no official fix for the other problems shared by Nightmare Eclipse.
Related news:
New Windows Defender ‘RoguePlanet’ zero-day grants SYSTEM privileges
Security Update: RoguePlanet, BitLocker Bypass, Chromium Zero-Day, and More Critical Threats Uncovered



