 InfoSecBulletin Cybersecurity for mankind
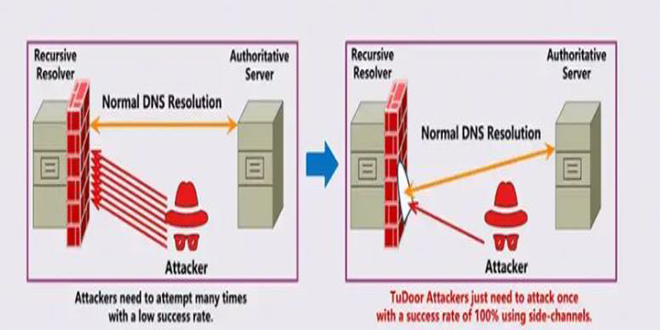
A new critical vulnerability in the Domain Name System (DNS) has been found. This vulnerability allows a specialized attack called “TuDoor” that can poison DNS caches, cause denial-of-service (DoS) attacks, and deplete resources, posing a significant threat to internet security.
Specialists have conducted experiments that confirm the feasibility of the TuDoor attack, revealing its serious implications in real-world scenarios. A striking total of 24 widely used DNS programs, including BIND, PowerDNS, and Microsoft DNS, have been found vulnerable to TuDoor. In less than a single second, attackers can execute cache poisoning or DoS attacks against these vulnerable resolvers using just a handful of precisely fabricated packets.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Researchers tested 16 Wi-Fi router models, 6 operating systems, 42 DNS services, and about 1.8 million open DNS resolvers. The study found that TuDoor could exploit 7 routers, 18 DNS services, and 424,652 open DNS resolvers.
The researchers followed best practices for responsible disclosure by informing all affected vendors of the vulnerabilities. 18 vendors, such as BIND, Chrome, Cloudflare, and Microsoft, confirmed the findings and discussed ways to fix the issues. 33 CVE identifiers were assigned to the vulnerabilities, and an online tool for their detection was suggested.
Collaboration among researchers, developers, and users is crucial to ensure a secure digital environment. We need constant vigilance to address new vulnerabilities like TuDoor. By working together, we can achieve innovation and protection simultaneously.



