 InfoSecBulletin Cybersecurity for mankind
StormWall projects a 170% increase in DDoS Attacks by the end of 2023 and urges businesses to implement mitigation strategies.
Leading cybersecurity provider, StormWall, has released a comprehensive report on the state of Distributed Denial of Service attacks (DDoS attacks) in Q1 2023. The report, based on an analysis of attacks on StormWall’s clients across various sectors, reveals a significant increase of 47% in DDoS attacks compared to the same period last year.
The findings, shared with Hackread.com, highlight a worrisome trend of botnet usage and a growing practice of smokescreening to conceal multi-vector attacks.
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The study reveals that attackers are increasingly targeting critical infrastructure and services, including logistical services, payment processing hubs, and banking systems, in an attempt to impact a larger number of users. The average attack strength reached a peak of 1.4 Tbps, and the longest attack lasted for 4 days.
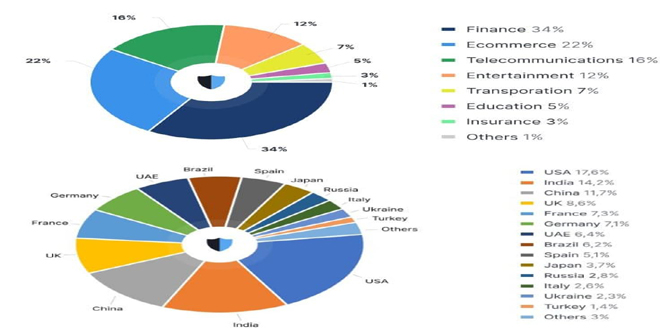
Among the sectors targeted, the financial industry experienced the highest number of attacks, accounting for 34% of the total and witnessing a staggering 68% increase compared to Q1 2022. E-commerce also faced significant challenges, enduring 22% of the attacks and experiencing a 51% increase from the previous year. Telecommunications remained a popular target, with 16% of the attacks and a 47% year-over-year increase.
The use of botnets in DDoS attacks continues to gain traction, with over 38% of attacks leveraging networks of compromised devices. Additionally, the practice of smokescreening, where DDoS attacks are used as decoys in multi-vector assaults, increased by 28% compared to the previous year.
The report also reveals that more destructive HTTP attacks are becoming increasingly accessible to run. As a result, 82.3% of DDoS attacks targeted the application layer (L7), while 11.7% were directed at the transport (L4) and network (L3) layers of the OSI model. DNS was targeted in 2.3% of the attacks, and the remaining 3.7% were aimed at other targets.
Geographically, the United States (17.6% attack share), India (14.2%), and China (11.7%) remain the most targeted countries. However, the United Arab Emirates saw a notable surge in attacks, with the proportion nearly doubling from 3.8% in Q1 2022 to 6.4% in the current year. Russia and Ukraine, on the other hand, experienced a decline in DDoS activity as hacktivism subsided.
Did you know that in 2021, the United States and China both held the position of being the top countries with the most exposed cloud servers due to misconfiguration? India ranked fifth in this regard. Read more…

StormWall’s report emphasizes the escalating threat of DDoS attacks, as evidenced by the significant rise in attack volume, strength, and duration. With threat actors constantly adapting their tactics and integrating DDoS attacks within multi-vector incidents, organizations need to address not only outages from overburdened servers but also data breaches, ransomware, and other associated threats.
Based on data analysis from client-targeted attacks, StormWall projects a further 170% increase in DDoS attacks by the end of 2023. In light of these alarming findings, the company strongly recommends that all businesses seek professional DDoS protection to safeguard their online assets in the upcoming year.



