Thursday , October 22 2026

Microsoft Authenticator
Microsoft Authenticator blocks suspicious MFA alerts by default

Microsoft has added a new security feature to the Authenticator app. This feature blocks suspicious notifications that occur during the account login process.

Microsoft Authenticator is an app that provides multi-factor authentication, password auto-fill, and password-less sign-in to Microsoft accounts.

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Anthropic says a Claude research model showed how the National Security Agency made seeds for five NIST elliptic curves in...
Read More
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

The Indian Computer Emergency Response Team (CERT-In), which is the government's cybersecurity arm, has issued a "critical" rated advisory after...
Read More
Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

MITRE released ATT&CK v20 adding nine Enterprise techniques that explain how attackers might target AI systems, steal app-specific passwords to...
Read More
MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Cybersecurity researchers at Palo Alto Networks’ Unit 42 have uncovered a sophisticated cyberattack targeting Fortinet network management infrastructure, involving the...
Read More
Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

When a user tries to log into an account with protected by multi-factor authentication (MFA), the Authenticator app sends a push notification to the user’s device to grant or deny access.

Alternatively, the app generates a temporary access code for users to manually log into their account.

ALSO READ:

Trial run of ‘Smart Parking’ app started at Dhaka

Hackers exploit push notifications by performing many login attempts on the target account, often at inconvenient times, to frustrate or tire the recipients.

If the tired user agrees to a request, the attacker can enter the account and change the login security settings to lock out the real user.

Microsoft added a security feature called “number matching” in May. It requires users to enter a number from the sign-in screen into their Authenticator app to approve the login.

Although this measure has reduced the effectiveness of MFA fatigue attacks, it doesn’t stop the generation of the annoying notifications themselves.
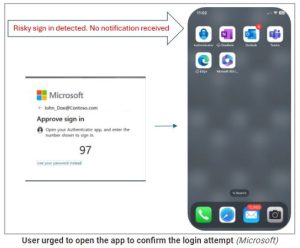
Microsoft has added new features to fight against malicious activity. These features examine login attempts for unfamiliar locations or signs of unusual activity, and block the related notifications.

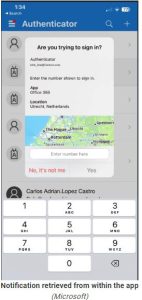
Instead, users receive a message that prompts to open the Authenticator app and enter a given code.

You can still see login notifications in the Authenticator App for review when needed.
Microsoft has blocked over six million MFA notifications believed to be from hackers since the new feature was rolled out in September.


Check Also

Qwen

Claude, DeepSeek, and Qwen AI agents combinedly used to hit gov.t across Asia

Chinese-speaking hackers have added Claude, Qwen, and DeepSeek to their hacking system to automate cyberattacks …