 InfoSecBulletin Cybersecurity for mankind
Multiple Versions:
“Security experts said LockBit previously released various versions of its ransomware:”
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

LockBit version 1.0 was released in January 2020 and originally known as “ABCD” ransomware.
LockBit version 2.0, aka “Red,” was released in June 2021 together with StealBit, the group’s primary data exfiltration tool.
LockBit Linux was released in October 2021 to infect Linux and VMWare ESXi systems.
LockBit version 3.0, aka “Black,” was released in March 2022 and leaked six months later by the group’s disgruntled developer, leading to multiple knockoffs.
LockBit Green was released in January 2023 and heralded as being a major new version, which security experts quickly dispelled, finding it to be a rebranded version of a Conti encryptor.
LockBit next-gen:
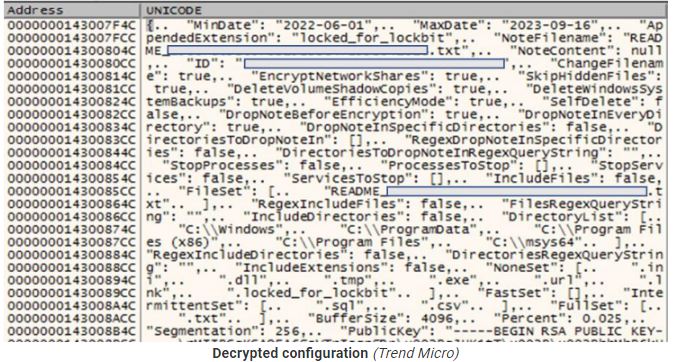
Trend Micro provides a JSON configuration file containing relevant execution parameters and operational flags.
The security firm says the new encryptor is in its final development stages, even though it doesn’t have all the features of previous versions, like the ability to spread on breached networks and print ransom notes. However, it already has most of the expected functionality.
It has three encryption modes (using AES+RSA): “fast,” “intermittent,” and “full.” ItIt supports three encryption modes (using AES+RSA), namely “fast,” “intermittent,” “full,” and “intermittent intermittent,” has custom file or directory exclusion, and can randomize the file naming to complicate restoration efforts.
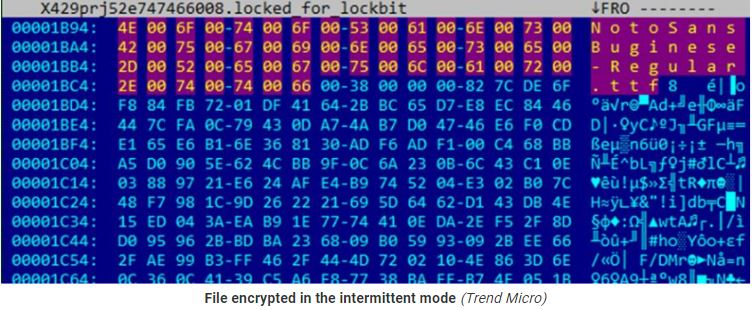
Additional options include a self-delete mechanism that overwrites LockBit’s own file contents with null bytes.
Trend Micro published a detailed analysis of the LockBit-NG-Dev malware, including its configuration parameters.
Source: Trend Micro research



