 InfoSecBulletin Cybersecurity for mankind
IT administrators should update any on-premises ScreenConnect servers due to reports of a critical vulnerability being exploited in the wild.
CVE-2024-1709 is an authentication bypass bug. It has a CVSS score of 10.0. This bug can be used to execute code and access sensitive data without needing the user to interact. It can be exploited with relatively simple attacks.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

ConnectWise, the company behind the remote desktop software, discovered a path traversal vulnerability with a CVSS score of 8.4. This vulnerability is now known as CVE-2024-1708.
Cloud customers have already received the updates, but on-premises customers need to take action.
“Partners that are self-hosted or on-premises need to update their servers to version 23.9.8 immediately to apply a patch,” the vendor said. “We’ve received notifications of suspicious activity that our incident response team has investigated.”
Separately, according to a US intelligence source, the initial access brokers currently exploiting the CVSS 10.0 bug will eventually sell it to ransomware actors.
“The sheer prevalence of this software and the access afforded by this vulnerability signals we are on the cusp of a ransomware free-for-all. Hospitals, critical infrastructure, and state institutions are proven at risk,” he warned.
“With remote access software, the bad guys can push ransomware as easily as the good guys can push a patch. And once they start pushing their data encryptors, I’d be willing to bet 90% of preventative security software won’t catch it because it’s coming from a trusted source.”
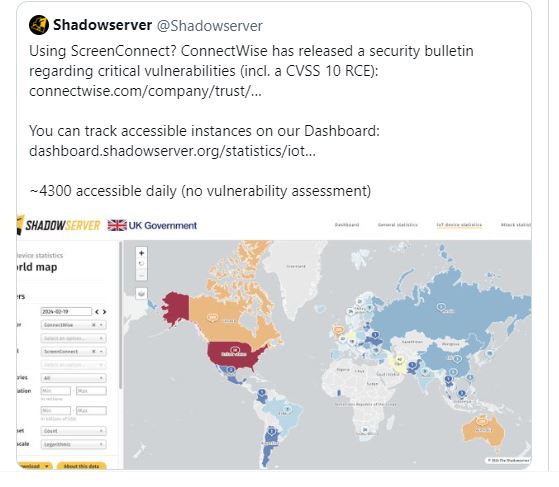
Around 3800 ConnectWise ScreenConnect instances are still vulnerable to exploitation of both bugs, according to a tweet from The Shadowserver Foundation yesterday.



