InfoSecBulletin Cybersecurity for mankind
The Indian Computer Emergency Response Team (CERT-In) has warned Adobe users about a high-risk cybersecurity issue. Adobe recently found serious security problems in various versions of their software, including Adobe Premiere Pro, Adobe InDesign, and Adobe Bridge.
CERT-In classifies the vulnerabilities as “HIGH” severity and advises users to act quickly to protect their systems by updating their Adobe software. If left unattended, attackers could use these vulnerabilities to cause memory leaks and run unauthorized code on targeted systems, resulting in serious consequences such as stolen data, system crashes, and unauthorized access to sensitive information.
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

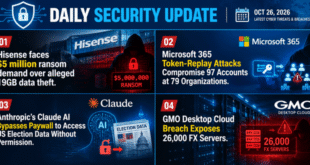
Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

In addition to Adobe Products, the CERT-In has also issued critical vulnerability warnings for IBM WebSphere application server and Joomla Content Management System.
According to CERT-In, several underlying issues are responsible for the vulnerabilities found in Adobe products:
Integer Overflow or Wraparound: This vulnerability occurs when an arithmetic operation surpasses the maximum capacity of the integer data type used to store the value, leading to unexpected behavior or crashes.
Heap-based Buffer Overflow: This arises when data surpasses the designated buffer capacity in the heap memory, potentially allowing attackers to execute unauthorized code.
Out-of-bounds Write and Read: These vulnerabilities occur when software reads or writes data beyond the allocated memory boundaries, leading to data corruption, crashes, or code execution.
Untrusted Search Path: This vulnerability arises when software searches for resources in untrusted directories, which attackers can exploit to execute malicious code.
IBM WebSphere Application Server Under Fire:
CERT-In has also reported a vulnerability in IBM WebSphere Application Server (CVE-2024-0215) that could allow Remote Code Execution (RCE) attacks. This means attackers could potentially exploit this flaw to execute malicious code on the server, granting them complete control of the system.
According to IBM, “a remote attacker could exploit this vulnerability to execute arbitrary code on the system with a specially crafted sequence of serialized objects.”
The bulletin applies to:
IBM WebSphere Application Server Traditional V9.0 or earlier versions
IBM WebSphere Application Server Network Deployment V8.5 or earlier versions
IBM has recommended updating to the following versions to address the vulnerability or fix the pack that contains the APAR PH61489.
For V9.0.0.0 through 9.0.5.20:
Upgrade to minimal fix pack levels as required by interim fix and then apply Interim Fix PH61489
–OR–
· Apply Fix Pack 9.0.5.21 or later (targeted availability 3Q2024).
For V8.5.0.0 through 8.5.5.25:
Upgrade to minimal fix pack levels as required by interim fix and then apply Interim Fix PH61489
–OR–
· Apply Fix Pack 8.5.5.26 or later (targeted availability 3Q2024).
Users can find detailed information and download the updates from the official IBM Security Bulletin.