 InfoSecBulletin Cybersecurity for mankind
IBM QRadar is a popular SIEM (Security Incident and Event Management) tool that organizations use to detect and monitor threats. It can be used in the form of a physical appliance, a software-only solution, or a virtual appliance. As of 2023, over 1,130 companies worldwide use IBM QRadar as part of their SIEM.
Recently, IBM discovered three new vulnerabilities in IBM QRadar. These vulnerabilities were related to cryptography, cross-site scripting (XSS), and information disclosure. IBM has released fixes for these vulnerabilities. The vulnerabilities were discovered by IBM’s Security Ethical Hacking team.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

IBM QRadar SIEM Flaw
CVE-2023-26276: Weak Cryptographic Algorithm:
This vulnerability exists due to the use of a weaker or expected cryptographic algorithm in the QRadar tool, which could allow a threat actor to decrypt highly sensitive information. This vulnerability was given a CVSS Score of 5.9 (medium)
ALSO READ:
Cisco AsyncOS Software Flaw Let Remote Hackers Launch XSS Attack
CVE-2023-26274: Cross-Site Scripting (XSS):
An attacker can exploit this vulnerability to embed arbitrary JS code in the Web UI that can alter the functionality that can lead to credentials disclosure through XSS on a trusted session. This vulnerability was given a CVSS Score of 4.6 (medium).
CVE-2022-34352: Information Disclosure
This vulnerability allows a delegated Admin tenant with a specific domain security profile to see other domain data.This vulnerability was given a CVSS Score of 6.5 (medium).
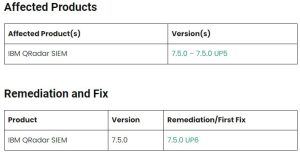
IBM recommended all its users patch their IBM QRadar SIEM by upgrading it to the latest version.
Source: IBM, GB hacker, vulners.com



