 InfoSecBulletin Cybersecurity for mankind
Hackers to exploit a flaw in Zimbra mail servers that are connected to the Internet. They send special emails that allow them to run commands on a weak server without needing to log in or get an employee to open a message.
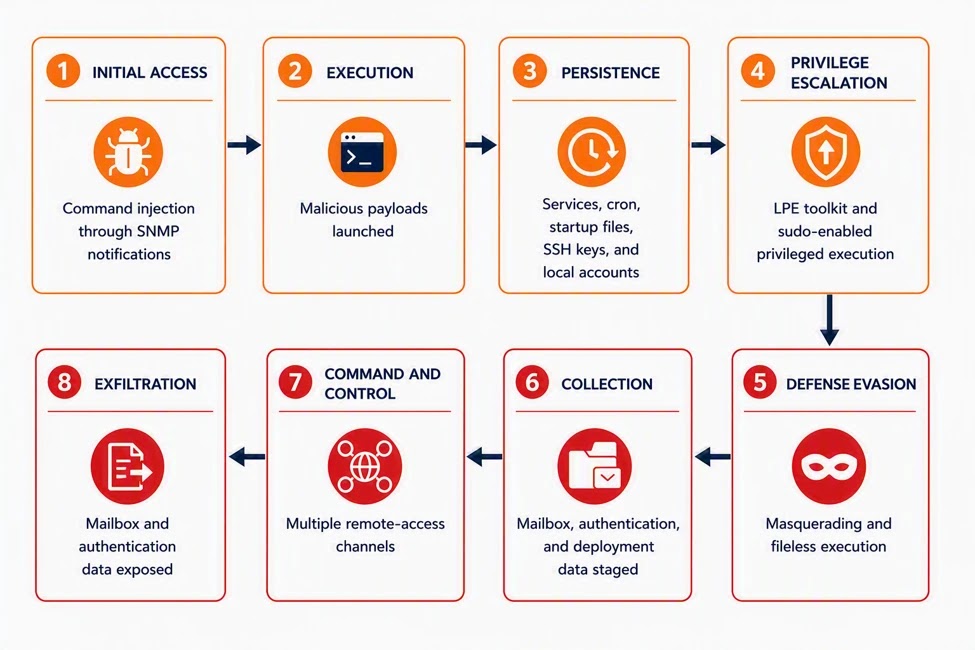
The focus is on CVE-2026-73570, a command-injection vulnerability with the server’s SNMP notification feature. It impacts systems that have the optional zimbra-snmp package and have SNMP notifications on, making a usual monitoring path a way in.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Microsoft Threat Intelligence found and tracked the attacks, discovering affected groups in many areas and industries. Microsoft said in a report said that attackers combined automated payload delivery with hands-on keyboard activity after gaining access.
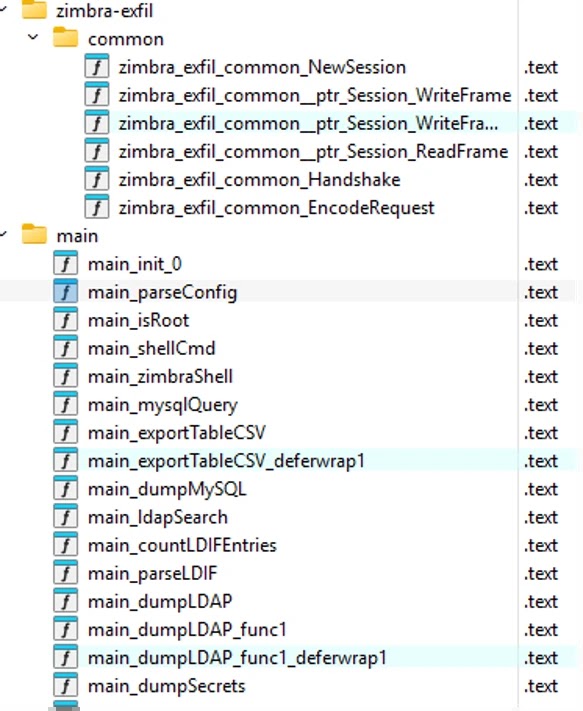
The effects go beyond one mailbox. Investigators found web shells, encrypted reverse connections, stolen login details, ongoing remote access tools, and efforts to gather mail data. This needs updates and checks in the organizations looked into by Microsoft.
TeamViewer Vulnerabilities
TeamViewer has released updates to fix five serious security problems in its Full Client, Host, and other parts for Windows, Linux, and macOS. The biggest flaw could let attackers get around remote-session rules and possibly run code on weak systems.
The company urged customers to update TeamViewer clients to version 15.82 or the latest version available. TeamViewer said it is not aware of public disclosure or active exploitation of the vulnerabilities in the wild.
| CVE ID | Vulnerability | Severity | CVSS |
|---|---|---|---|
| CVE-2026-19743 | Path traversal in local IPC | High | 7.8 |
| CVE-2026-92368 | Heap buffer overflow in .tvs playback |
High | 7.8 |
| CVE-2026-92369 | TOCTOU race in Windows installer | High | 7.3 |
| CVE-2026-92370 | Improper access control | High | 8.8 |
| CVE-2026-92371 | Improper link resolution | High | 7.0 |
Organizations need to find systems using TeamViewer Full Client or Host and upgrade to version 15.82 or the newest supported release.



