InfoSecBulletin Cybersecurity for mankind
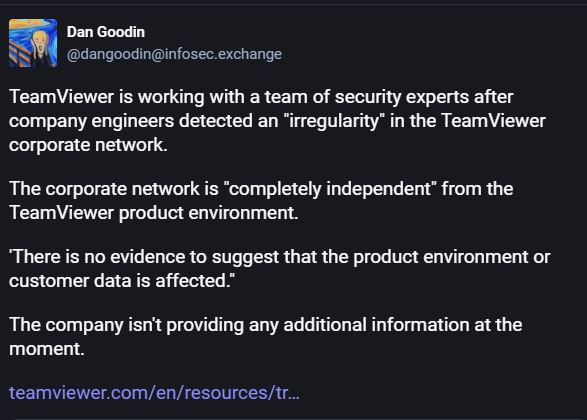
In a statement On Wednesday, 26 June 2024, team viewer said, “our security team detected an irregularity in TeamViewer’s internal corporate IT environment. We immediately activated our response team and procedures, started investigations together with a team of globally renowned cyber security experts and implemented necessary remediation measures.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

TeamViewer’s internal corporate IT environment is completely independent from the product environment. There is no evidence to suggest that the product environment or customer data is affected. Investigations are ongoing and our primary focus remains to ensure the integrity of our systems.
Security is of utmost importance for us, it is deeply rooted in our DNA. Therefore, we value transparent communication and will continuously update the status of our investigations as new information becomes available.”
The company will be transparent about the breach and provide updates on the investigation as more information is available.
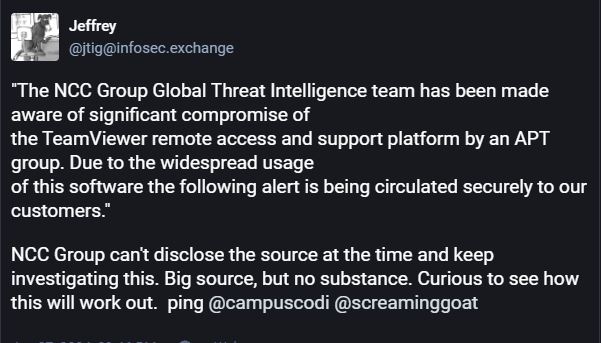
The breach was initially reported by IT security professional Jeffrey on Mastodon. He shared parts of an alert from the Dutch Digital Trust Center, a web portal used by the government and Dutch corporations to share cybersecurity information.
The register reported, Brett Callow, a threat analyst at Emsisoft, mentioned that the US-based Health Information Sharing and Analysis Center (H-ISAC) issued a warning to the health sector regarding the continuous exploitation of TeamViewer. Callow explained how healthcare operators should react to this alert.
That memo reads:
The Health Information Sharing and Analysis Center June 27 issued a threat bulletin alerting the health sector to active cyberthreats exploiting TeamViewer. H-ISAC recommends users review logs for any unusual remote desktop traffic. Threat actors have been observed leveraging remote access tools, H-ISAC said. The agency recommends users enable two-factor authentication and use the allowlist and blocklist to control who can connect to their devices, among other measures.
HEALTH-Isac is also saying Teamviewer is compromised, attributing it to APT29 (Cozy Bear):
“On June 27, 2024, Health-ISAC received information from a trusted intelligence partner that APT29 is actively exploiting Teamviewer. Health-ISAC recommends reviewing logs for any unusual remote desktop traffic. Threat actors have been observed leveraging remote access tools. Teamviewer has been observed being exploited by threat actors associated with APT29.”
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)