InfoSecBulletin Cybersecurity for mankind
Infosecbulletin’s daily cyber security update is a daily basis security updates across the globe. This aim is to inform the readers todays happenings in cyber world. Using various ways the information is collected and only the headlines are shown here. Users are advised to read out the full report for more information from the link attached with each headlines.
Attackers are using a modified version of Minesweeper to target financial organizations in Europe and the U.S. They are using a remote access tool called SuperOps RMM. The attack has been attributed to UAC-0188 by CERT-UA.
Daily Cyber security update for 14.11. 2026

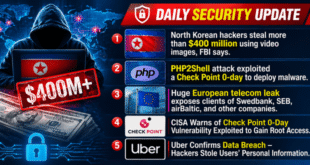
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Trellix discovered that cybercriminals used fake antivirus websites pretending to be Avast, Bitdefender, and Malwarebytes to spread info-stealers that aimed at Android and Windows users.
A new advanced ATM malware called EU ATM Malware has been found in Europe. It can infect around 60% of ATMs globally and has a reported success rate of 99%.
Researchers are warning about new phishing methods that use Cloudflare Workers, HTML smuggling, and generative AI to bypass security and steal user credentials.
In 2023, the FTC identified Best Buy and Geek Squad as the most impersonated brands, receiving 52,000 reports. Amazon was the second most impersonated brand, with 34,000 reports, followed by PayPal with 10,000 reports.
Cisco fixed a serious security issue in the web-based management interface of the Firepower Management Center software. The vulnerability is known as CVE-2024-20360 and has a CVSS score of 8.8.
SingCERT reported 9 critical vulnerabilities in WordPress plugins like WordPress Copymatic, Pie Register, Hash Form Drag & Drop Form Builder, and others.
Hackers are using cloud storage services like Amazon S3, Google Cloud Storage, and IBM Cloud Object Storage to host harmful websites and spread SMS phishing scams.
The White House is taking steps to improve data routing security for more than 50% of federal agencies’ IP addresses by the end of 2024. This is being done to prevent advanced attacks that manipulate the Border Gateway Protocol.