Thursday , October 1 2026
u mobile
The data, claimed to include personally identifiable information (PII), is on sale for US$5,000 (RM23,380) in Bitcoin. — GOH GAIK LEE/The Star

Nacsa investigates
Malaysia Telco U Mobile Four Million user data allegedly Breached

Malyasian National Cyber Security Agency (Nacsa) is investigating a possible data breach that exposed the data of four million U Mobile subscribers.

The data, which claimed to contain personal information like names, addresses, MyKad numbers, andThe data, which may include personal information like names, addresses, MyKad numbers, and mobile phone numbers, was put up for sale on July 16 for US$5,000 (RM23,380) in Bitcoin on a well-known forum that sells leaked information.

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

Google has said that hackers are using two serious Citrix NetScaler security holes to get root access, set up hidden...
Read More
Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is alerting people about a major flaw in MikroTik RouterOS. This could...
Read More
CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

Apple has launched iOS 26.7.1 and iPadOS 26.7.1 to fix a serious zero-day flaw that it believes might have been...
Read More
Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

The JadePuffer ransomware group is attacking Azure users with agent-based attacks that gather information, steal passwords, and damage key components. The...
Read More
JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

The 5th Edition of InfoSecCon-2026, a premier cybersecurity-focused event, has been successfully completed with the participation of cybersecurity professionals, technology...
Read More
“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

Microsoft has fixed a serious security flaw in Azure AI Foundry that could let bad actors gain privilege escalation. The...
Read More
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Amazon Web Services cannot restore access to its cloud-computing facility in Bahrain and ‌one of three data-hosting zones in the...
Read More
AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

A threat actor is allegedly offering a private remote code execution exploit for Fortinet FortiGate SSL VPN appliances, claiming that...
Read More
Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

Anthropic is making a new Claude feature called “Money.” It's a separate tab in the mobile app. The new interface...
Read More
Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

GhostCode is a new phishing kit that changes a regular Microsoft 365 sign-in into an account theft. It doesn't need...
Read More
GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

However, the posted sample looked incomplete, with some entries missing MyKad numbers and addresses.

Nacsa, the government agency in charge of cybersecurity in Malaysia, is investigating the data’s legitimacy and has asked U Mobile for more details.
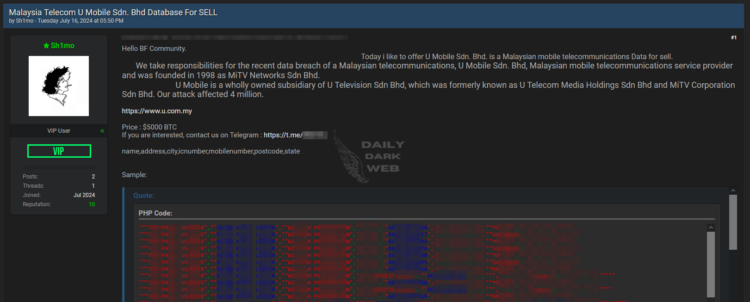
   Source: Daily Drak web

In a statement, U Mobile said “it’s aware of the alleged data breach. It said: “We are actively investigating this situation. We are working closely with the authorities to address this matter effectively and will provide relevant updates once confirmed information becomes available. We wish to assure all stakeholders that we take matters of cybersecurity and data privacy seriously and are dedicating all resources to thoroughly investigate the situation.”

(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)


Check Also

India: C-DOT Launches 14 Local Quantum-Safe Technologies

India is making its communication systems safer and stronger by launching 14 local quantum products. …