InfoSecBulletin Cybersecurity for mankind
Banks and financial institutions are undergoing rapid digital transformation, which has improved customer services. However, this shift has also increased cyber threats and vulnerabilities. As a result, cyber resilience is crucial to protect financial systems.
Bangladesh Bank, in its role as a regulator, has unveiled a Cyber Security Framework V- 1.0 specifically tailored for banks and financial institutions under its jurisdiction. This initiative aims to enhance cyber security governance and fortify defenses against cyber threats. The framework is structured around five essential pillars of the NIST Cyber Security Framework: Identify, Protect, Detect, Respond, and Recover.
Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

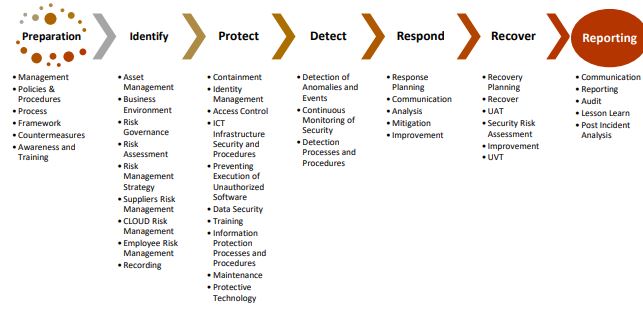
It controls primarily draw from ISO 27001, national ICT Security Policies, and ICT Security Guidelines for Banks and NBFIs, along with other recognized international standards. It’s important to note that this framework establishes baseline cyber security standards and controls intended to meet the minimum safeguarding requirements against cyber threats.
This framework is applicable to banks, non-bank financial institutions (NBFIs), mobile financial service providers (MFSPs), payment service providers (PSPs), payment system operators (PSOs), and other financial service organizations. These entities will collectively be referred to as “The Organization.”
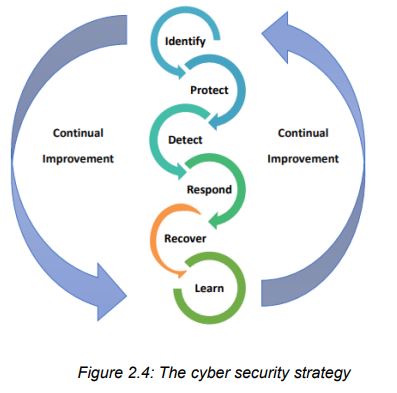
The objectives of this framework are to establish a minimum baseline for management of Cyber Security in the Organization based on the following key areas to:
a) Protecting Financial Stability
b) Detecting and Responding to Cyber Threats
c) Create a common approach for addressing cyber security;
d) Achieve an appropriate maturity level of cyber security practices;
e) Define roles and responsibilities of relevant parties;
f) Address Cyber Security practices with due diligence;
g) Ensure security and privacy requirements;
h) Develop stakeholders‘ awareness to protect information in cyber environment;
i) Ensure a secure environment for data processing;
j) Ensure best practices (industry standard) of the usage of technology.
k) Building a Cyber security Culture
Bangladesh Bank has taken the initiative to accept any suggestions to enrich the “Cyber Security Framework for Banks and Non-Bank Financial Institutions” version 1.0 draft.
The prepared draft framework has already been uploaded on Bangladesh Bank website https://www.bb.org.bd/en/index.php/about/draftguide.
Anyone can suggest any through e-mails at ([email protected] and [email protected]) by 08/10/2024.