 InfoSecBulletin Cybersecurity for mankind
The gentlemen ransomware group targets various industries of Bangladesh. In an advisory Bangladesh e-Government Computer Incident Response Team (BGD e-GOV CIRT) warned that the ransomware operates under a Ransomware-as-a-Service (RaaS) model and is capable of rapidly spreading across corporate networks, encrypting Windows and Linux systems, network storage devices and VMware ESXi environments.
The biggest worry for Bangladesh is that the malware can take over a Domain Controller and possibly spread ransomware all over a company in just minutes.
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

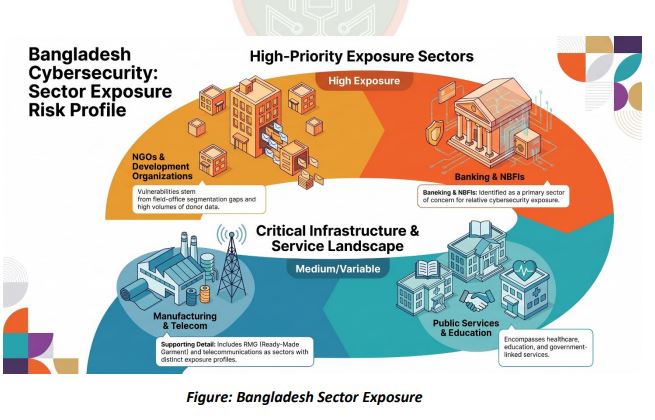
Bangladesh on the Threat Radar
According to CIRT, an NGO in Bangladesh was named on The Gentlemen’s extortion site in July 2026. The attackers said they would release stolen information on their site.
The event shows that more Bangladeshi companies are at risk from ransomware groups that steal data and demand money. CIRT found that areas like banking, finance, telecom, manufacturing, clothing, healthcare, education, NGOs, and government groups could be good targets.
A Single Compromised System Could Trigger a Network-Wide Attack
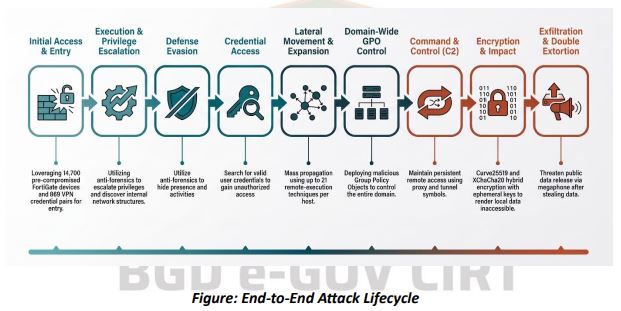
The Gentlemen ransomware is very dangerous because it can move easily through compromised networks. Once attackers get into one computer, they can use different tools like SMB, PsExec, WMI, PowerShell, Remote Scheduled Tasks, and Windows Services to infect more devices.
The danger becomes significantly greater if attackers obtain control of an organization’s Active Directory or Domain Controller.
CIRT said that hackers can use Group Policy and admin rights to spread ransomware to many systems, which could lead to the encryption of the entire company in just minutes.
Double Extortion Makes More Dangerous
The Gentlemen do not just encrypt files. They use a common double-extortion method: first, they steal important data, then they encrypt systems. If the ransom is not paid, victims are threatened with sharing the stolen data.
This creates two simultaneous risks for Bangladeshi organizations:
Operational disruption: critical systems and files become inaccessible.
Data exposure: confidential customer, employee, financial, business and beneficiary information may be leaked.
NGOs and development groups could face big problems if their databases are hacked. These databases may hold private information about helpers, donors, workers, and projects.
Vulnerable VPNs, Firewalls and Remote Systems Could Open the Door
CIRT pointed out that internet-connected systems are a great risk. Attackers can take advantage of weaknesses or get in through open VPN gateways, firewalls, backup systems, and hypervisor management tools.
Weak credentials, stolen passwords, outdated software and poorly configured Active Directory environments can further increase the risk.
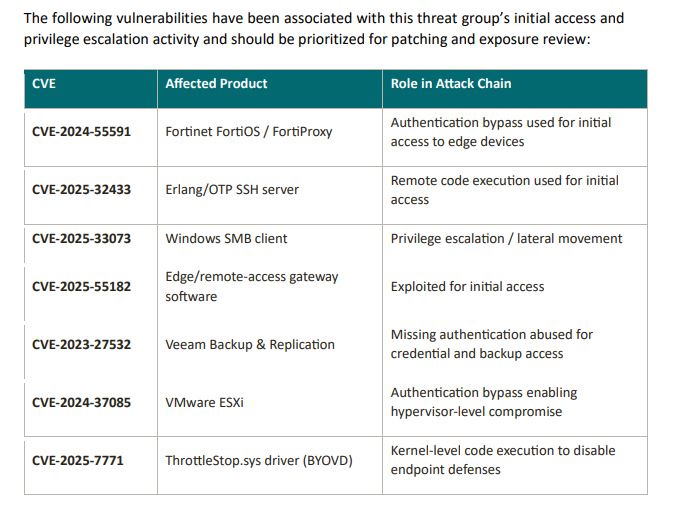
CIRT asks organizations to closely watch technologies like Fortinet FortiOS/FortiProxy, Veeam Backup & Replication, and VMware ESXi, among others.
CIRT also cited threat intelligence indicating that the operators may have access to approximately 14,700 previously compromised FortiGate devices and 969 verified brute-forced VPN credential pairs.
CIRT Urges Immediate Defensive Measures
CIRT has urged organizations to take immediate steps to reduce their exposure. Key recommendations include:
Patch internet-facing firewalls, VPNs, backup systems and hypervisor infrastructure.
Enable phishing-resistant multi-factor authentication for remote and administrative accounts.
Strengthen security around Active Directory and Domain Controllers.
Disable SMBv1 and enable SMB signing.
Isolate VMware ESXi management interfaces from ordinary network traffic.
Enable endpoint detection and response and tamper protection.
Monitor for abnormal credential dumping and network-scanning activity.
Maintain offline, immutable or air-gapped backups.
Regularly test backup restoration procedures.
Segment critical systems to prevent rapid lateral movement.
The Warning for Bangladesh
The Gentlemen ransomware is a big threat to Bangladesh. It can quickly spread from one infected device and disrupt whole company networks. Its mix of RaaS, stealing data, double extortion, using stolen credentials, and attacking Domain Controllers makes it very dangerous. The presence of a Bangladeshi group on its extortion site shows the need for organizations to improve their internet-connected systems, secure accounts, Active Directory, network separation, and offline backups.
Related Topic:
How Bangladeshi’s Ogrs Be Evaluated By Newly Launched NRS & CIRS
Bangladesh Launches (CIRS) and National ICT & Cyber Security Rating System (NRS)
The Gentlemen Ransomware Attacks Windows, Linux, NAS, BSD, and ESXi Systems



