 InfoSecBulletin Cybersecurity for mankind
A critical command injection flaw in Node Multimedia Routers (MMRs) may let meeting participants run arbitrary code on vulnerable systems. CVE-2026-22844 is a highly critical vulnerability with a CVSS score of 9.9, indicating an urgent need for immediate action.
Zoom Command Injection Vulnerability:
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

A command injection flaw is found in Zoom Node MMR versions prior to 5.2.1716.0, impacting Zoom Node Meetings Hybrid (ZMH) and Zoom Node Meeting Connector (MC) setups. The vulnerability requires only network access and low-level privileges to exploit, with no user interaction necessary.
The vulnerability targets MMR modules running versions earlier than 5.2.1716.0, so identifying and patching these versions is crucial. Zoom’s Offensive Security team discovered this issue.
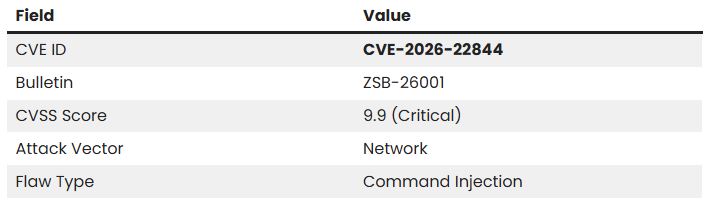
Zoom urges administrators to promptly update MMR modules to version 5.2.1716.0 or later.
The company released guidance in its Managing Updates for Zoom Node support documentation, offering step-by-step instructions for patching Zoom Node infrastructure.



