 InfoSecBulletin Cybersecurity for mankind

Developer ElDavoo unveils a new open source tool named “WhatsApp Crypt Tools” . It makes it easier to access WhatsApp’s end-to-end encrypted backups, which hold chat histories, media, and metadata in SQLite databases or ZIP files.
The wa-crypt-tools program, available on GitHub, decrypts and encrypts .crypt12, .crypt14, and .crypt15 files from WhatsApp and WhatsApp Business, provided users supply the required key file or 64-character key.
Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

The tool supports protobuf for modern formats and works well with forensics suites like Whapa for advanced analysis. Users can easily deploy it without local setup. Google Colab provides a browser notebook for quick tests, making it ideal for non-technical users or cloud workflows.
Locally, install via pip with “python -m pip install wa-crypt-tools” for stable builds or the GitHub URL for development versions; Jupyter notebooks suit data scientists familiar with the environment.
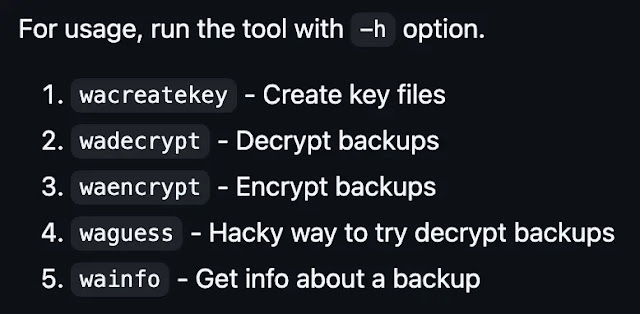
Decryption shines with the wadecrypt command: “wadecrypt encrypted_backup.key msgstore.db.crypt15 msgstore.db” yields a readable SQLite file after loading the Crypt15 key.
Encryption via waencrypt remains beta, recommending a reference crypt15 file for reliability, as in “waencrypt –reference msgstore.db.crypt15 key msgstore.db new.crypt15.” Additional utilities like wainfo inspect backups, wacreatekey generates keys, and waguess attempt brute-force guesses.
Cybersecurity experts can use this tool for mobile investigations, retrieving data from modified Android devices at /data/data/com.whatsapp/files/key.
Research papers examine disappearing messages and injection attacks in E2EE apps, while YouTube and XDA tutorials guide users on recovering .crypt15 backups through ADB pulls. It also supports undocumented .mcrypt1 Google Drive files.
Decryption requires key passwords; these only secure key retrieval from WhatsApp servers. Newer app versions (tested last on 2.24.x) have compatibility issues, including crypt15 failures that need force flags or developer help on Telegram.
Experts suggest using secure backups without passwords and self-managed keys to protect data. This tool allows data recovery without rooting devices and highlights WhatsApp’s strong encryption when keys are kept safe.



