 InfoSecBulletin Cybersecurity for mankind
Microsoft will assign Common Vulnerabilities and Exposures (CVE) numbers to important vulnerabilities found and fixed in their cloud services. This improves transparency and security by publicly disclosing vulnerabilities that can be fixed without user intervention.
Microsoft’s decision to assign CVE numbers to cloud service vulnerabilities, regardless of whether customer action is required, shows their commitment to transparency as cloud services become more important for businesses and infrastructure. By sharing information about vulnerabilities, even those that don’t need customer action, Microsoft hopes to promote collaboration for learning and improvement among the company and its partners.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

This increased transparency can lead to several benefits, including:
Enhanced Security: Sharing vulnerability information allows Microsoft and its partners to improve security measures.
Improved Resilience: By learning from past vulnerabilities, the industry as a whole can better prepare for and handle future threats, ensuring the resilience of critical infrastructure.
Greater Customer Confidence: Being aware that Microsoft is actively identifying and addressing vulnerabilities, even those not directly affecting users, can increase trust in their cloud services.
“As our industry matures and increasingly migrates to cloud-based services, we must be transparent about significant cybersecurity vulnerabilities that are found and fixed,” stated Lisa Olson, Senior Program Manager at Microsoft. “By openly sharing information about vulnerabilities that are discovered and resolved, we enable Microsoft and our partners to learn and improve. This collaborative effort contributes to the safety and resilience of our critical infrastructure.”
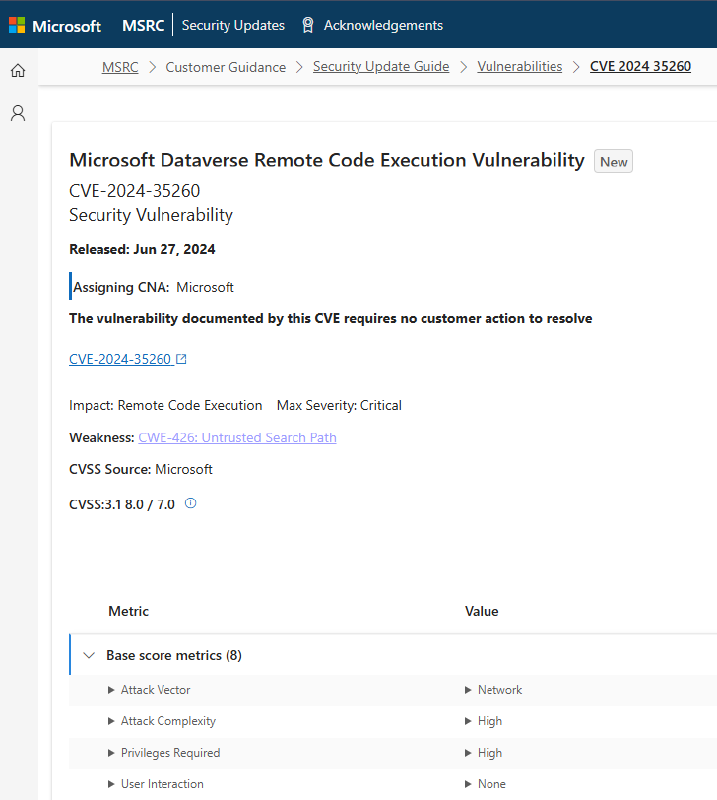
For instance, Microsoft recently issued an advisory for CVE-2024-35260, a vulnerability in Microsoft Dataverse that has been resolved.
This change doesn’t require customers to do anything, but it shows that Microsoft is making a positive effort to improve transparency and security in their cloud services. Microsoft’s commitment to openly discussing vulnerabilities shows their dedication to continuously improving the security of their cloud services.



