InfoSecBulletin Cybersecurity for mankind
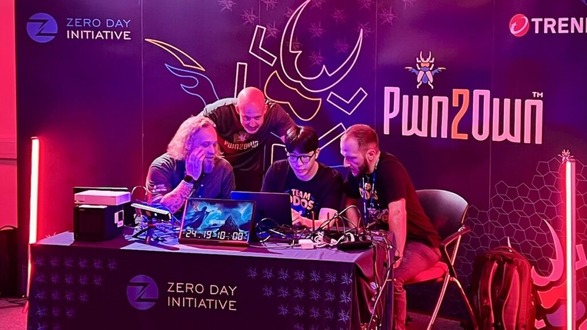
Security researchers earned a combined $1,315,250 in cash rewards after exploiting 90 zero-day vulnerabilities during the first two days of Pwn2Own Ireland 2025, organized by Trend Micro’s Zero Day Initiative (ZDI) in Cork.
On Day 1, participants demonstrated 34 new vulnerabilities, earning $522,500 by breaching printers, NAS devices, routers, and smart home products. The top $100,000 “SOHO Smashup” prize went to researchers who chained exploits targeting QNAP Qhora-322 routers and QNAP TS-453E NAS devices. Other highlights included $50,000 for attacks on the Synology ActiveProtect DP320 and Sonos Era 300, alongside successful hacks on Home Assistant Green, Philips Hue Bridge, Canon, and HP printers.
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10

On Day 2, hackers uncovered 56 additional zero-days, collecting $792,750. The standout moment was Ken Gannon (Mobile Hacking Lab) and Dimitrios Valsamaras (Summoning Team) breaching the Samsung Galaxy S25 via a five-bug exploit chain, earning $50,000 and 5 Master of Pwn points. Other teams, including CyCraft Technology, Verichains Cyber Force, and Synacktiv, won $20,000 each for compromising QNAP, Synology, and Philips Hue devices.
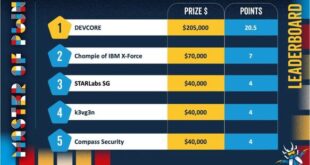
The Summoning Team currently leads the Master of Pwn leaderboard with 18 points and $167,500 in earnings.
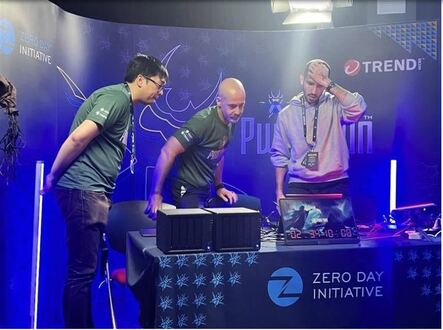
The contest—co-sponsored by Meta, Synology, and QNAP—runs from October 21–24, featuring challenges across smartphones, NAS devices, printers, messaging apps, smart home gear, and wearables.
On the final day, researchers aim for the ultimate prize: a $1 million reward for a WhatsApp zero-click remote code execution exploit. Vendors now have 90 days to patch all reported vulnerabilities before public disclosure.