 InfoSecBulletin Cybersecurity for mankind
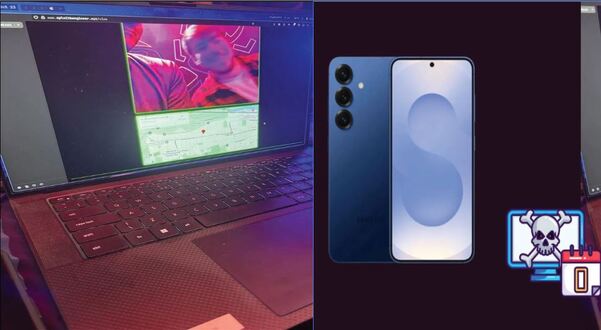
At Pwn2Own Ireland 2025, researchers Ben R. and Georgi G. from Interrupt Labs demonstrated their success in exploiting a zero-day vulnerability in the Samsung Galaxy S25. They gained complete control of the device, allowing them to activate the camera and track the user’s location.
The exploit, revealed on the event’s final day, highlights ongoing security challenges in flagship Android smartphones despite rigorous testing by manufacturers.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

The Interrupt Labs team found a bug in the Galaxy S25’s software that failed to validate inputs, letting attackers bypass security and run code remotely.
Samsung Galaxy S25 0-Day Vulnerability:
By crafting malicious inputs, the researchers demonstrated how an adversary could silently hijack the device without user interaction, a technique that evaded Samsung’s defenses during the live contest.
A previously undisclosed vulnerability allowed persistent access, turning the premium smartphone into a surveillance tool that can capture photos, videos, and real-time GPS data.
Experts note that such flaws often arise in multimedia or system libraries, where rapid feature development outpaces security hardening.
Ben R. and Georgi G. won $50,000 and 5 Master of Pwn points for their advanced exploit chain, which helped the event achieve a total payout of $2 million from 73 unique zero-days.
Pwn2Own, run by the Zero Day Initiative, rewards people for responsibly reporting flaws to help vendors like Samsung fix them.
Samsung has yet to issue a specific statement on this Galaxy S25 exploit, but historical patterns suggest an imminent security update will address it, similar to recent fixes for other Android zero-days.
Users should turn on automatic updates and check official channels for patches, as unaddressed exploits can leak sensitive data in actual attacks.



