 InfoSecBulletin Cybersecurity for mankind
Cybercriminals now offer services and products to other cybercriminals is a significant development in the last two decades.
Cybercrime-as-a-service has made it easier for criminals to get into cybercrime, allowing them to specialize and commit crimes on a larger scale. For instance, instead of coding malware, a criminal can buy it in underground markets.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

According to cyber threat intelligence firm Intel471, Botnet operators distribute malware by offering spamming services to send it to victims. The victims’ email addresses are bought from vendors who trade and sell data breaches. Spam and malware need to be sent from and hosted somewhere on the internet. This shows that connectivity is a basic requirement for cybercrime because criminals need internet access to commit crimes.
ISPs are important in stopping harmful activity. They accept abuse complaints from various sources, such as law enforcement agencies and security researchers. If a machine on their network is spreading malware, it can be shut down and the offender’s account can be terminated.
If a service provider doesn’t respond to an abuse request, it becomes difficult to cut cybercriminals off from the internet. This is especially true when the organizations providing connectivity are unresponsive shell companies with false registration information. These companies offer “bulletproof” hosting (BPH), which is highly desired by malicious hackers, spammers, malware distributors, and botnet operators. BPH allows cybercriminals to engage in harmful activities for a certain period of time without being shut down or facing significant risks.
Stopping BPH online is difficult. Providers use tricks to avoid being permanently removed from the internet, adapting to local laws and preventing certain illegal activities to avoid shutdown attempts.
More resilient and obfuscated network arrangements may allow for riskier types of crime, such as credit card fraud or phishing pages. BPH providers often operate in regions where law enforcement may have less interest or few resources to investigate their operations.
BPH providers make it hard to take down and report abuse by using complex technical arrangements. This includes buying IP address ranges from other bulletproof providers, using fast-flux hosting, and routing malicious traffic through changing proxy and gateway servers in different areas. BPH services can also be persistent, as some have been run by known threat actors for a decade or longer.
The goal of cybersecurity defenders is to stop cyber attacks as soon as possible. A crucial aspect is to prevent communication with malicious domains and services, which are often hosted on BPH providers. If an organization can identify the IP addresses or autonomous systems of BPH providers, they can block them from accessing their network, preventing employees from clicking on harmful links.
BPH services consistently change their ASs and IP ranges. Tracking these changes can allow defenders to quickly block access to new networks. For example, if a threat actor that has long been known to run BPH services and creates a new front company linked to a new but very small AS, it’s possible to say with high confidence that any of those IP addresses are likely to be malicious and thus safe to completely block. This type of high confidence and high-fidelity threat intelligence is possible because of the collection of historical technical intelligence and continued adversary monitoring.
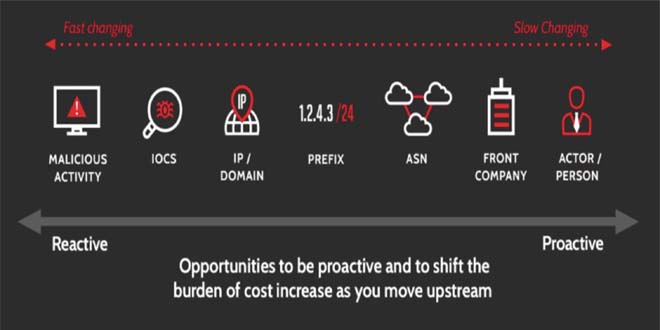
The chart below shows how technical indicators related to BPH change. IOCs and IP/domains change frequently, but BPH services can still be tracked for real-time intelligence. By monitoring changes in BPH infrastructure, security teams can stay ahead of criminals and proactively prevent cyber threats. There are also more stable data points, like ASNs, front companies, and threat actors, that can be used to accurately predict malicious activity. Click here to find more.



