 InfoSecBulletin Cybersecurity for mankind
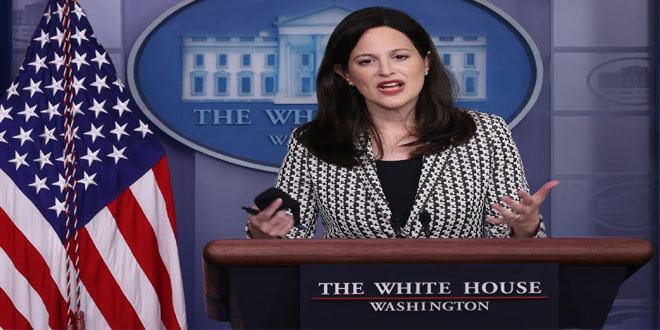
Anne Neuberger, Deputy National Security Adviser for Cyber and Emerging Technology at the White House, suggested that this initiative is a response to the increasing global threat of ransomware attacks. She stated that the United States has been targeted in around 46% of these incidents.
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

ALSO READ:
Starting Wednesday, international discussions during the summit will also focus on strategies to block the funds used by ransomware groups to finance their operations, Reuters first reported.
“Ransomware is an issue that knows no borders,” Anne Neuberger, the White House’s deputy national security adviser for cyber and emerging technology, told reporters during a briefing on Monday. “And as long as there’s money flowing to ransomware criminals … the problem will continue to grow.”
The Counter-Ransomware Initiative is taking steps to enhance its members’ ability to combat these attacks, in addition to its no-ransoms pledge.
Members of the initiative will use artificial intelligence to analyze blockchains — immutable digital ledgers of payment activity — to help identify ransomware payments flowing through cryptocurrency platforms. They will also maintain a shared blacklist of ransomware gangs’ cryptocurrency wallets, making it easier for members to identify illicit payment flows and alert their domestic cryptocurrency firms to block or freeze those transactions. And members will pledge to help each other respond to any ransomware attacks affecting government agencies or vital sectors like health care, energy and communications.
Two new information sharing platforms will help members exchange data about ransomware operators, their tools, and techniques. Lithuania operates one platform, while Israel and the United Arab Emirates jointly run the other. The platforms serve different purposes and countries are encouraged to use the one they prefer. The U.S. expects each country to share at least one threat information every week.
The group’s agenda for the next year will consist of raising awareness of where these hackers operate, where they’re able to rent or steal access to computer servers and “how to implement accountability on that,” according to the senior administration official.
The biggest antagonists in cyberspace — Russia, China, Iran and North Korea — aren’t members of the initiative and have repeatedly ignored U.S. pleas to stamp out malicious cyber activity emanating from within their borders. There is no clear plan for getting them to crack down on cybercrime.



