Sunday , November 15 2026
Ransomware
Ransomware red button on keyboard, 3D rendering

Corvus threat intel report
Ransomware Attacks Up More Than 95% Over 2022

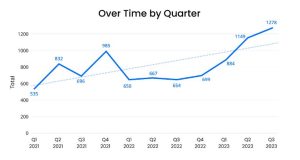
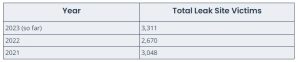
In its Q2 2023 Global Ransomware Report, Corvus noted a significant resurgence in global ransomware attacks, which has continued through the third quarter. Now, with two months remaining in the year, the number of ransomware victims in 2023 has already surpassed what was observed for 2021 and 2022. If the trajectory continues, 2023 will be the first year with more than 4,000 ransomware victims posted on leak sites (2,670 in 2022).

           Corvus Threat Intel report

2023 has already seen more ransomware victims than all of 2021 and 2022 combined. If this trend continues, there could be over 4,000 ransomware victims posted on leak sites this year.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical
     Corvus Threat Intel report
Note that this is not the complete picture. Victims who are listed on leak sites usually do not pay or delay paying a ransom. However, a significant portion of victims, estimated to be between 27% – 41%, promptly pay the demands of threat actors and therefore are not seen on leak sites.
As a result, the total number of businesses affected by ransomware could be approximately 5,500 – 7,000 in 2023.

Factors Contributing to the Global Ransomware Surge

CL0P Mass Exploits Peaked:

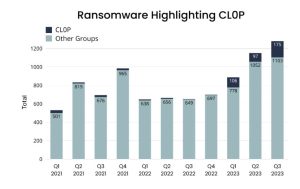
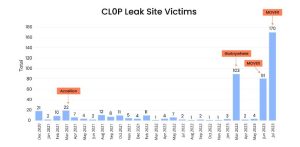
CL0P, a previously quiet ransomware group, became active in Q1 by exploiting GoAnywhere file transfer software and impacting over 130 victims. In Q2, they targeted MOVEit file transfer software using a zero-day vulnerability, affecting 264 victims. This single vulnerability accounted for 9% of Q2’s total and 13% of Q3’s victims, significantly contributing to an increasing victim count.

However, even without CL0P, ransomware numbers increased by 5% compared to the previous quarter and 70% compared to the previous year in Q3.

The graph below illustrates the significant impact of a single group like CL0P, which was once relatively quiet.

Prior to 2023, CL0P only had a small number of ransomware victims. Now, they make up a considerable share of the total. A single opportunity for mass exploitation can lead to record-breaking results for a ransomware group.

        Corvus Threat Intel report
The grey bars show the activity of ransomware groups, excluding CL0P. These bars have been increasing steadily in 2023. Even without CL0P, ransomware activity is increasing.
Each quarter of this year has been higher than the previous one. Based on past trends, Q4 is expected to be worse than Q3.
     Corvus Threat Intel report
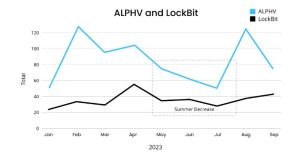
LockBit and ALPHV (BlackCat) reduced the number of victims on their leak sites by around 50% from April to July 2023. However, the latest numbers from late Q3 and early Q4 indicate that ransomware groups are returning to their usual activities and are expected to cause more harm in Q4.

  Corvus Threat Intel report


Check Also

948

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

OpenAI says that an automated system found and confirmed 948 different Linux kernel security issues …