 InfoSecBulletin Cybersecurity for mankind
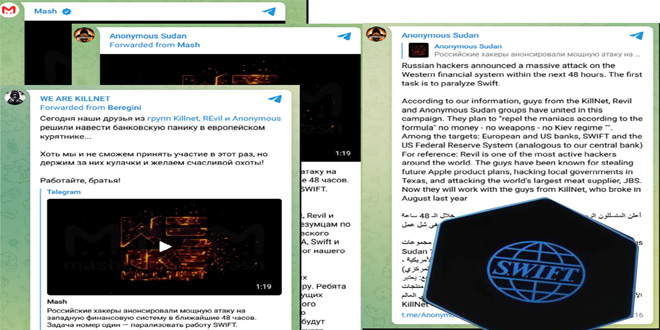
Three hacking groups, Killnet, Anonymous Sudan, and REvil, have threatened to launch a “destructive” attack against the European financial system, starting with the SWIFT international communications system. The attack is expected to take place within the next 48 hours.
The groups are reportedly motivated by political reasons, as they are angry at Europe’s involvement in the Ukraine war. They have threatened to target European banks and other financial institutions, as well as the US Federal Reserve.
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

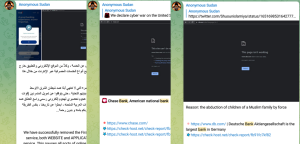
Security researchers have warned that the attack could have a significant impact on the global economy. They have urged financial institutions to be on “high alert” and to take steps to protect themselves.
ALSO READ:
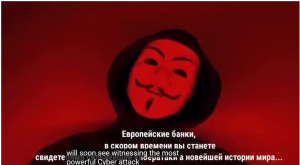
The video outlining the attack cites REvil’s expertise in the European banking structure. It also calls on “all active groups” to “engage in destructive activities” against the European financial sector.
SWIFT has not yet responded to the threat.
Key points:
- Three hacking groups have threatened to launch a cyberattack against the European financial system.
- The attack is expected to take place within the next 48 hours.
- The groups are reportedly motivated by political reasons.
- Security researchers have warned that the attack could have a significant impact on the global economy.
- SWIFT has not yet responded to the threat.
Analysis:
The threat of a cyberattack against the European financial system is a serious one. The SWIFT system is an essential part of the global financial infrastructure, and a disruption to it could have a significant impact on the economy.
The fact that the threat is coming from Russia-based hacking groups is also concerning. Russia has a history of using cyberattacks as a weapon, and the timing of this threat is particularly worrying, given the ongoing conflict in Ukraine.
It is important for financial institutions to be on high alert and to take steps to protect themselves from cyberattacks. They should also be prepared for the possibility of disruptions to the SWIFT system.
The global community needs to work together to deter and prevent cyberattacks. This includes sharing information about threats and vulnerabilities, and working to strengthen the security of critical infrastructure.
Twitter video link: Click



