 InfoSecBulletin Cybersecurity for mankind
After months of silence, the notorious cybercrime and hacking forum, BreachForums, has resurfaced under new management. ShinyHunters, a well-known hacking group, has seized control of the revived platform, sending shockwaves through the cybersecurity community and raising concerns among global law enforcement agencies.
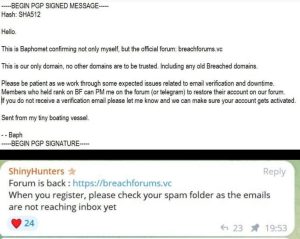
The announcement of BreachForums’ return came from Baphomet, one of the administrators of the original forum, via a PGP-signed message on Telegram. Baphomet, an active figure within the hacking community, left little doubt about the authenticity of the message, although skepticism remains due to the possibility of a honeypot operation.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

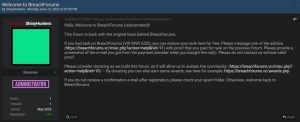
Adding to the unfolding situation, a Telegram account using the alias ShinyHunters (@shinycorp) has emerged alongside Baphomet, taking charge of communicating with former users of BreachForums. This account has already begun sharing information and updates related to the forum’s operations, attracting attention from potential members and concerned individuals alike.
BreachForums, in its previous incarnation, served as a notorious hub for cybercriminals to exchange stolen data, discuss hacking techniques, and engage in illicit activities. Now under the control of ShinyHunters, the forum’s resurgence has raised serious concerns in the cybersecurity community.
ShinyHunters has gained infamy for their involvement in multiple high-profile data breaches, often targeting organizations to steal sensitive information for financial gain. Their modus operandi involves selling user data on both Clearnet and the dark web.
The return of BreachForums under ShinyHunters’ control has ignited fears of an increase in cyberattacks, data breaches, and facilitation of illegal activities on the platform. Law enforcement agencies and cybersecurity experts worldwide are closely monitoring the situation and urging organizations and individuals to remain vigilant regarding their online security.
In the past, BreachForums faced closure following the arrest of its owner, Conor Brian Fitzpatrick, also known as Pompompurin or Pom, after he had created it as an alternative to the seized RaidForums. The forum remained offline, with members gathering in a Telegram group called “The Jacuzzi” to discuss its future. The FBI was unable to seize the forum’s domain, thus keeping it out of their reach.
ShinyHunters gained prominence in 2020 through their involvement in major data breaches, such as those affecting Tokopedia, a popular Indonesian online marketplace, and Microsoft’s GitHub repository. They are notorious for targeting organizations with large user bases and stealing personally identifiable information (PII), login credentials, and financial details.
ALSO READ:
Trend Micro Unleashes the Power of Generative AI in Vision One Platform
While the true identities of ShinyHunters remain unknown, their activities and the scale of the breaches they have orchestrated have raised serious concerns about cybersecurity and data protection.
One alleged member of ShinyHunters, Sébastien Raoult, was arrested in June 2022 at Rabat international airport and identified as a 21-year-old French citizen. In January 2023, Raoult, also known as Sezyo, was extradited to the United States and pleaded not guilty to the charges against him. However, despite Raoult’s arrest, concerns persist regarding the reemergence of cyber threats associated with the ShinyHunters group.
Considering ShinyHunters’ history, organizations previously targeted by this group must take immediate action to strengthen their security systems. Implementing robust protocols and enhancing security measures are crucial steps to protect user data and mitigate the risk of future attacks.



