 InfoSecBulletin Cybersecurity for mankind
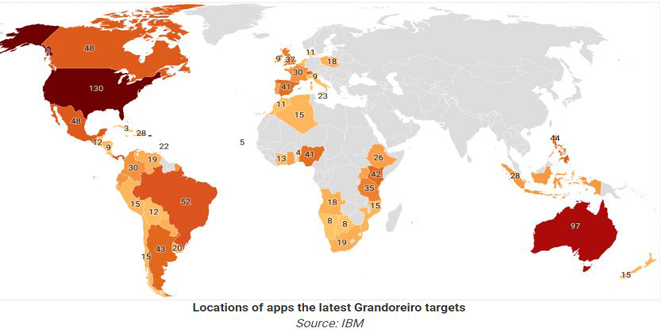
The banking trojan “Grandoreiro” is spreading widely through a phishing campaign in over 60 countries, aiming at customer accounts of about 1,500 banks.
In January 2024, a joint international law enforcement operation involving Brazil, Spain, Interpol, ESET, and Caixa Bank revealed the disruption of a malware operation. The malware had been targeting Spanish-speaking countries since 2017, resulting in $120 million in losses.
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

IBM’s X-Force team says that Grandoreiro has been operating on a large scale since March 2024, and is now targeting English-speaking countries. It is believed that it is being rented to cybercriminals through a Malware-as-a-Service (MaaS) model.
The trojan has been updated with new powerful features and improvements, suggesting that its creators were not stopped by previous efforts to catch them.
New campaigns:
Since multiple threat actors rent the malware, the phishing lures are diverse and crafted specifically for the organizations a particular cybercriminal is targeting.
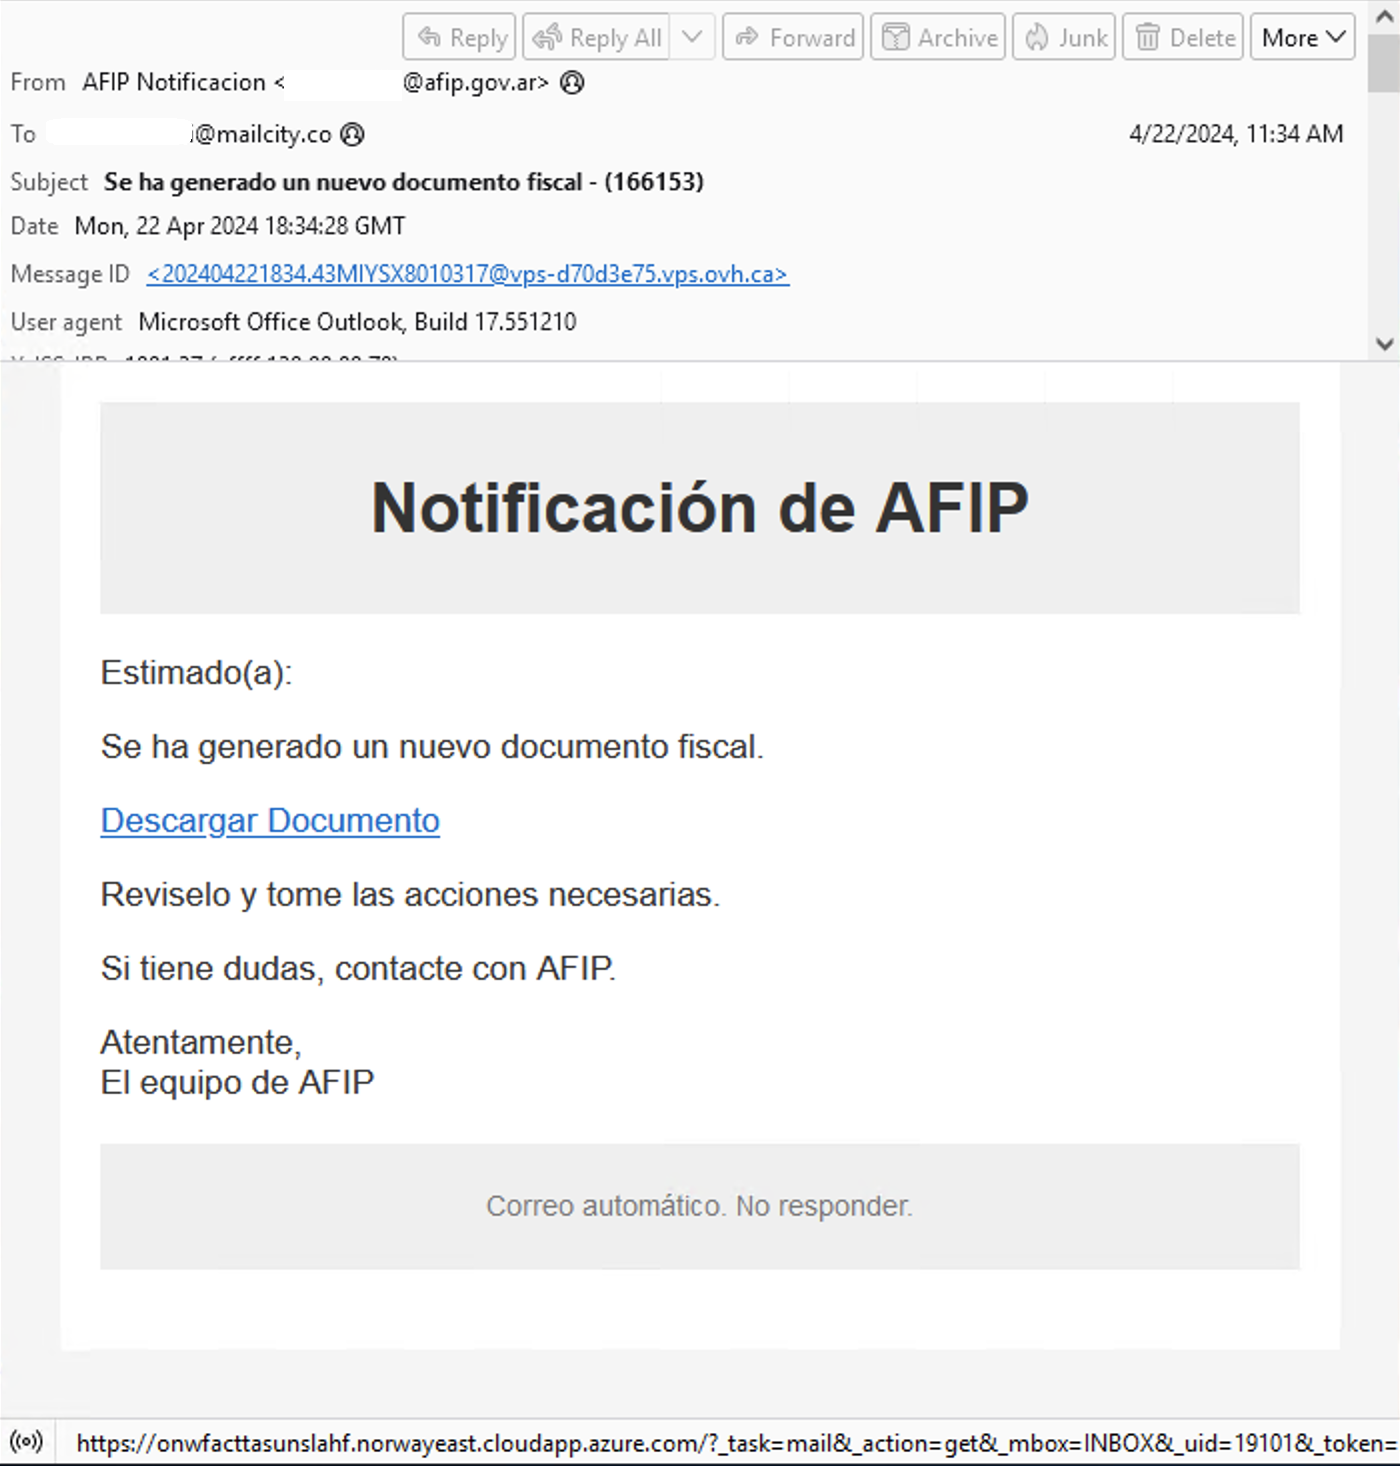
IBM has detected phishing emails pretending to be government agencies in Mexico, Argentina, and South Africa. The targeted organizations include tax administration agencies, revenue services, and federal electricity commissions.
The emails are written in the recipient’s language, include official logos and formats, and ask them to click on links to see invoices, account statements, or tax documents.
When users click on those emails, they are redirected to an image of a PDF that triggers the download of a large (100 MB) executable file called Grandoreiro loader. Click here to read full report.



