 InfoSecBulletin Cybersecurity for mankind
SonicWALL SSL-VPN provides secure remote access to an organization’s internal network and resources through an encrypted SSL connection. This kind of VPN is great for giving employees and partners secure access to internal applications and data from remote locations.
A hacker is selling a $1000 exploit that targets SonicWALL SSL-VPN systems. This exploit supposedly lets attackers get around two-factor authentication (2FA) and access records from the RADIUS base, which can lead to unauthorized access to sensitive information.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

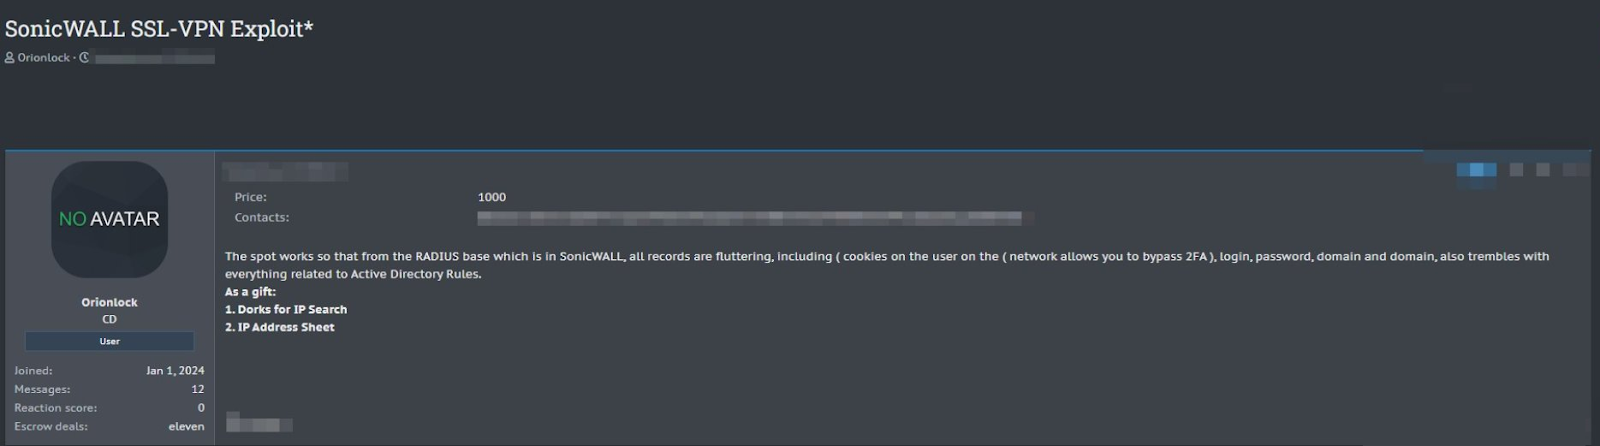
Exposed Information Includes:
User cookies
Login credentials
Passwords
Domain information
Active Directory Rules details
Previous SonicWALL Exploits
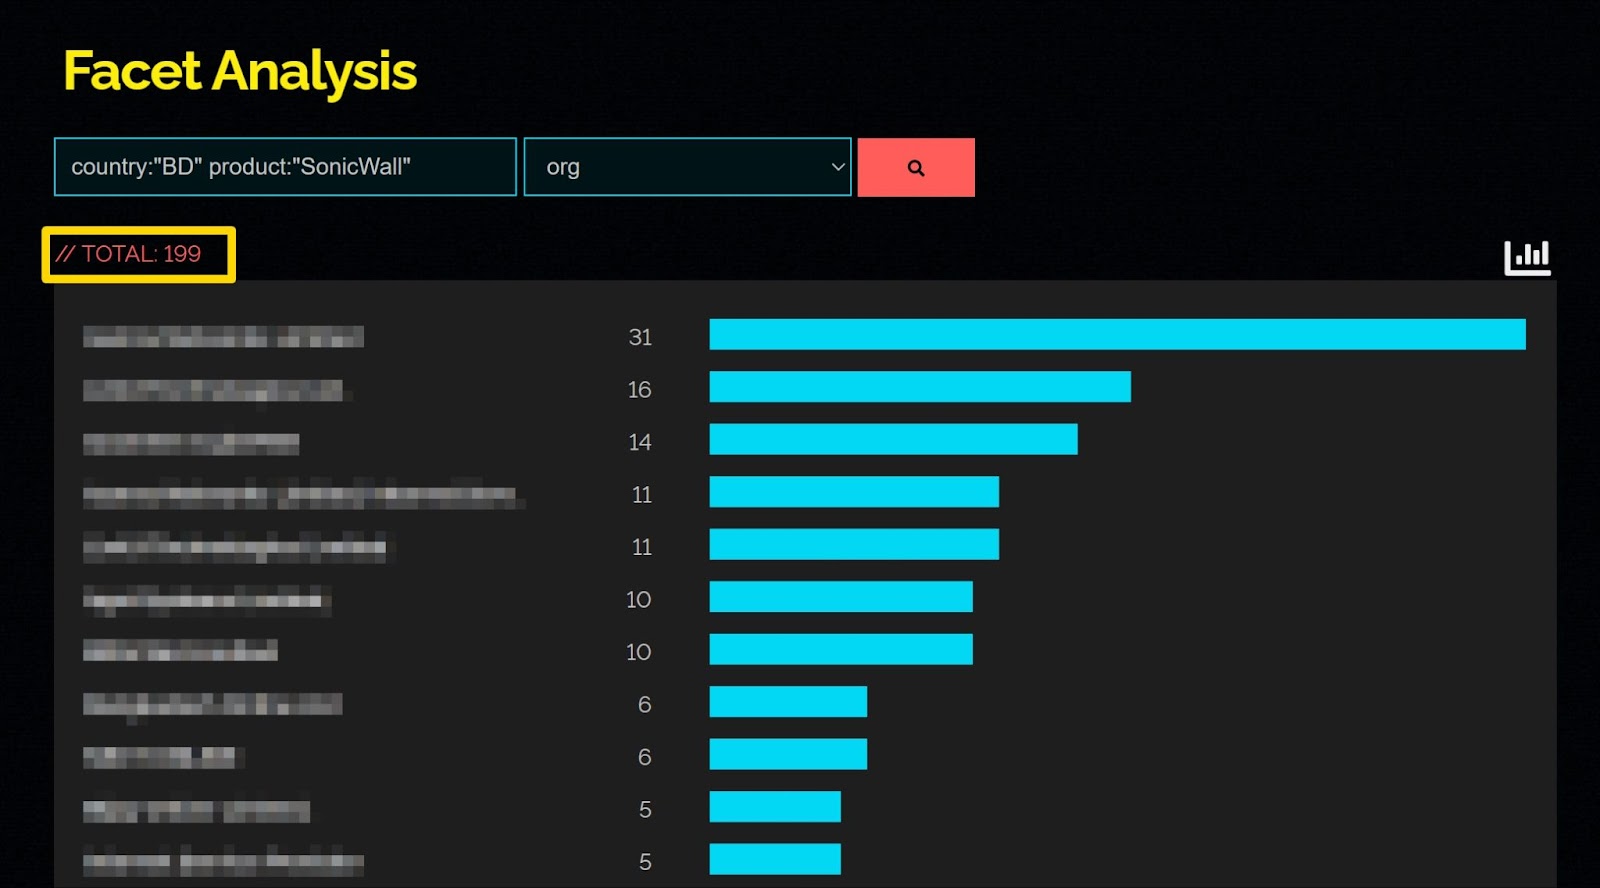
BSCI said, according to Shodan search, there found 199 IP using SonicWall SSL-VPN on various organization in Bangladesh but may have more, they may be the target point of the bad actors if cant take stern action to secure.
According to Bangladesh cyber security intelligence (BSCI), The exploit is capable to bypasses 2FA, compromising a key security measure, Accesses RADIUS base records to retrieve sensitive data.
In 2021, hackers breached SonicWall’s SMA 100 series VPN appliances through zero-day vulnerabilities and a critical vulnerability was found in SonicWall’s SMA and SRA products, enabling attackers to gain control over affected systems by executing arbitrary code in 2029.
It’s important to quickly deal with security issues and keep all network security products updated with the latest patches.
Over a million users have been affected by the info stealer. Their data has been sold on the dark web, including sensitive information from corporations, financial institutions, and government organizations.
Hackers can use stolen credentials and an exploit called SonicWALL SSL-VPN to access classified information and cause data breaches. They can also launch ransomware attacks on organizations.
BCSI recommends staying alert and constantly checking their security systems for any strange activity, around the clock.



