Monday , October 26 2026
fox

Kaspersky report
New “Coyote” Trojan Targets 61 Brazilian Banks

Banking Trojan developers are always finding new ways to spread malware and infect victims. Kaspersky found a new malware that targets users of over 60 banks in Brazil. It caught the attention because of its advanced infection method using various technologies, different from known banking Trojan infections.

The malware uses the Squirrel installer to spread and uses NodeJS and a newer programming language called Nim as a loader to infect systems. Kaspersky named this new Trojan “Coyote” because coyotes hunt squirrels. The Nim language is described as a “statically typed compiled systems programming language that combines successful concepts from mature languages like Python, Ada, and Modula.” The use of less popular and cross-platform languages by cybercriminals is a trend we identified in the report on Crimeware and financial cyberthreats for 2024.

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools
Forget old Delphi and MSI:
Banking Trojans often utilize the Delphi language or MSI installers as a common method for initial infection. This is a well-known trend among malware creators in the cybersecurity community.
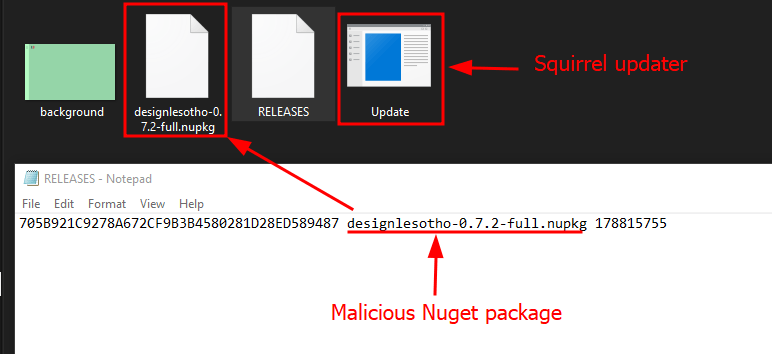
Coyote does things a little differently. Instead of going down the usual route with MSI installers, it opted for a relatively new tool for installing and updating Windows desktop applications: Squirrel. As the authors explain, “Squirrel uses NuGet packages to create installation and update packages, which means that you probably already know most of what you need to create an installer.”
              Source: Securelist

By using this tool, Coyote hides its initial stage loader by presenting it as an update packager.

Source: Securelist
The Node.js loader script:
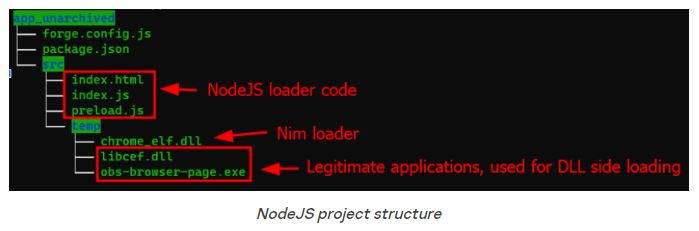
When Squirrel is used, it runs a NodeJS application with Electron. This application runs obfuscated JavaScript code (preload.js). Its main task is to copy all executable files from a local folder named temp to the user’s captures folder in the Videos folder. Afterward, it runs a signed application from that folder.
   Source: Securelist
The team found several executables being used, such as Chrome and OBS Studio. The banker is loaded by sideloading a DLL dependency of these executables. In all cases, the libcef.dll library is used for DLL sideloading. Click here to read the full report.
Source: Securelist

Check Also

Qwen

Claude, DeepSeek, and Qwen AI agents combinedly used to hit gov.t across Asia

Chinese-speaking hackers have added Claude, Qwen, and DeepSeek to their hacking system to automate cyberattacks …