InfoSecBulletin Cybersecurity for mankind
Apple has released an urgent security update for all its mobile devices to fix a serious zero-day vulnerability being exploited in a targeted attack describes as an “extremely sophisticated attack” against specific individuals.
CVE-2026-20700 is a serious vulnerability that prompted Apple to release iOS 26.3 and iPadOS 26.3 to protect users from unauthorized code execution.
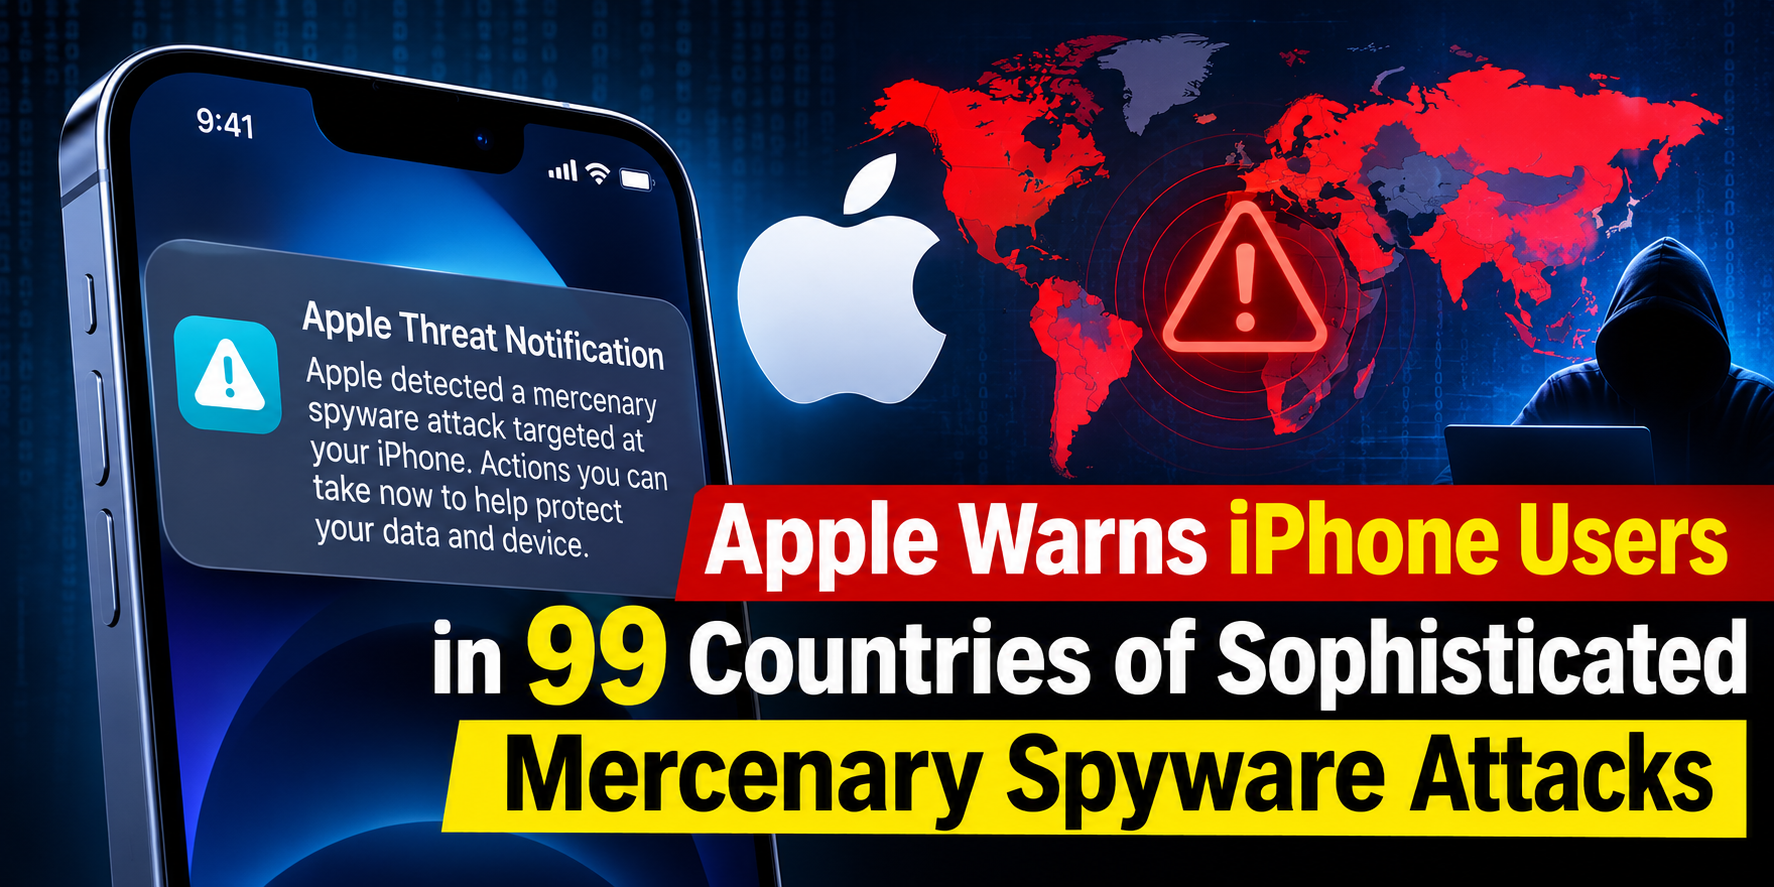
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks
Daily Cyber security update for 31.10. 2026
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

While Apple rarely details active campaigns, the advisory for CVE-2026-20700 contains a warning. The company confirmed it is “aware of a report that this issue may have been exploited in an extremely sophisticated attack against specific targeted individuals.”
The terms “sophisticated” and “targeted” usually refer to state-sponsored spying or commercial spyware. Google’s Threat Analysis Group (TAG) found this, indicating the exploit was likely aimed at journalists, dissidents, or diplomats, not the general public.
The vulnerability is in dyld, Apple’s Dynamic Link Editor, which loads shared libraries and frameworks when apps start.
Because dyld operates at such a low level, a vulnerability here is particularly dangerous. Apple notes that the flaw allows for Arbitrary Code Execution (ACE), stating that “an attacker with memory write capability may be able to execute arbitrary code.”
Apple’s update notes suggest that CVE-2026-20700 is linked to a larger exploit chain. They also disclosed two additional vulnerabilities—CVE-2025-14174 and CVE-2025-43529—were released due to this report, indicating that attackers combined several weaknesses to circumvent security measures.
The vulnerability affects a broad range of modern Apple devices. The patch applies to:
iPhone: iPhone 11 and later.
iPad Pro: 12.9-inch (3rd gen+), 11-inch (1st gen+).
iPad Air: 3rd generation and later.
iPad: 8th generation and later.
iPad mini: 5th generation and later.
Due to confirmed exploitation, this is an urgent update. Users should go to Settings > General > Software Update and install iOS 26.3 or iPadOS 26.3 immediately to protect against this advanced threat.