 InfoSecBulletin Cybersecurity for mankind
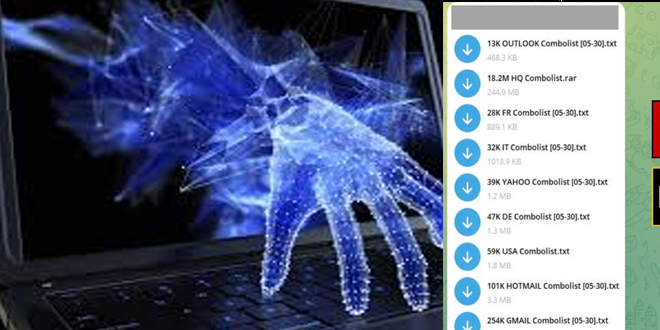
A big data breach was found with a combolist containing 122GB of data containing 361 million unique email addresses taken from thousands of Telegram channels.
The dataset contains passwords and websites linked to them. It reveals a lot of new data that has been added to the breach alert service called Have I Been Pwned (HIBP).
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Troy Hunt reported a discovery last week made by an anonymous researcher. The dataset includes 151 million email addresses not previously listed in the service, with 2 billion lines in 1,748 files. This shows that Telegram is widely used for sharing sensitive and illicit data.
Telegram is a messaging platform that offers privacy features. It lets users create channels to share information anonymously. Some people use this feature to distribute data from breaches. These data collections, also known as “combolists,” contain combinations of email addresses or usernames with passwords. These combolists are used in attacks to gain unauthorized access to accounts.
Data sent to Hunt came from 518 Telegram channels and had different sizes. Some files were very large, with millions of rows. The biggest files seemed to be a result of info stealer malware. This malware captured login information when people entered it on compromised computers. Hunt made sure the data was real by contacting HIBP subscribers and confirming that the stolen login information was accurate.
Responses from subscribers varied when contacted. Some recognized old passwords that had been used before, while others confirmed new and previously unseen data. For instance, one subscriber recognized passwords that had been used for different services over the past five years, and another identified credentials related to their daughter’s old Epic Games account. These verifications highlight the legitimacy of the data and the continued risk of credential theft.
Credential stuffing attacks use these combolists to access large numbers of accounts, which is a major threat to users. Various websites, such as Nike, Footlocker, and an Italian tire retailer, have confirmed that the stolen data includes email addresses, showing that many users are affected.
Given the severity of this breach, users are advised to take immediate action to secure their accounts:
Create new and unique passwords for all accounts.
Use a reliable password manager to create and save strong passwords.
Use two-factor authentication (2FA) whenever you can.
Check your accounts regularly for any unusual activity and turn on alerts for any unauthorized access attempts.
Update all your devices with the latest security patches.



