InfoSecBulletin Cybersecurity for mankind
The Singapore Land Authority (SLA) has announced that the personal details of around 70,000 people were leaked after someone accessed a cloud system managed by IBM, their tech provider.
IBM was chosen to help with and keep up SLA’s Singapore Titles Automated Registration System (Stars) and eLodgment System (ELS), which are important for registering property titles and submitting property documents in the city. As part of this job, the company handled the setup and testing for the two systems.
Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

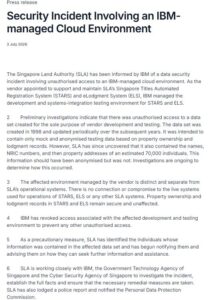
On 3 July 2026, SLA announced that IBM told them about the incident. Early checks showed that a dataset made only for development and testing had been accessed without permission.
The dataset, made in 1998 and updated over the years, was supposed to have only fake and hidden testing data about property ownership. But, SLA found out that the dataset also included names, NRIC numbers, and property addresses of the people involved at that time.
“This information should have been anonymised but was not,” the agency said, adding that investigations are ongoing to determine how this occurred.
SLA noted that the affected environment is “distinct and separate” from its operational systems, with no connection to, or compromise of, the live systems that run Stars, ELS or any other SLA systems. Property ownership and lodgement records remain secure and unaffected, it added.
IBM has cut off access to the affected area to stop any more unauthorized entry. Meanwhile, SLA has found the people whose information was in the dataset. They have started telling them and guiding them on how to get more information and help.
The agency is teaming up with IBM, the Government Technology Agency, and the Cyber Security Agency of Singapore to find out what happened and to take action. They have also made a police report and informed the Personal Data Protection Commission. They are telling people to stay alert for phishing emails, fake websites, text messages, and phone calls from those pretending to be government agencies or other groups.
“We apologise for the concern and inconvenience this incident may cause,” SLA said.
In April 2025, Toppan Next Tech, a printing company for DBS Bank and the Singapore Bank of China, suffered a ransomware attack. The attacker stole customer data. About 8,200 DBS customers, mainly those with DBS Vickers trading accounts and Cashline loans, and around 3,000 Bank of China customers might be affected.
A year earlier, in August 2024, a hacker broke into Mobile Guardian, a tool for managing mobile devices used in Singapore’s schools. The hacker wiped the iPads and Chromebooks of around 13,000 students from 26 secondary schools. After this, the Ministry of Education took the software off all student devices and ended its deal with the supplier.