InfoSecBulletin Cybersecurity for mankind
Cybersecurity Researcher Jeremiah Fowler uncovered and reported to Express VPN a publicly exposed database that was neither password-protected nor encrypted. The database contained 102,215 documents totaling approximately 79GB.
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

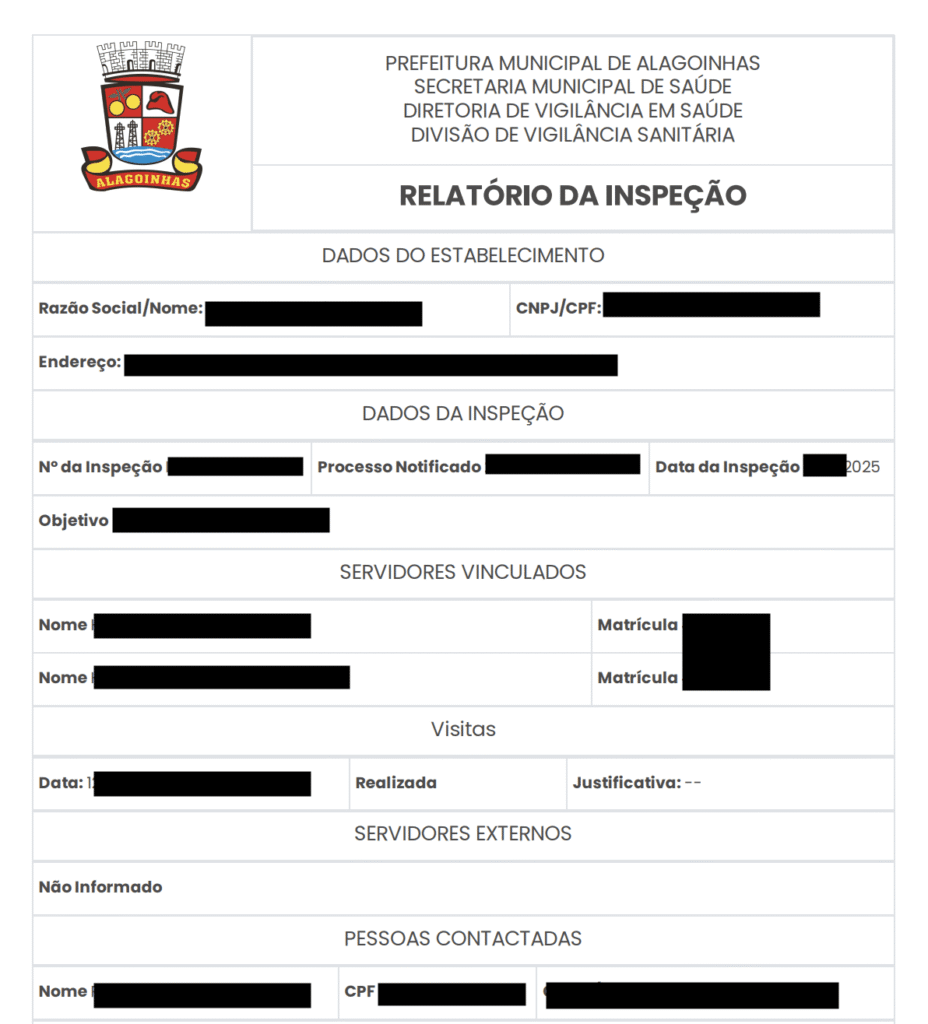
Jeremiah Fowler said, I saw a lot of sensitive information. This includes personal information like names and CPF/CNPJ numbers, contact details, home addresses, applications for licenses and permits, and documents related to health and safety rules. There were also inspection reports, papers proving compliance, complaints, two compressed backup files, and other items linked to public health monitoring and regulation enforcement.
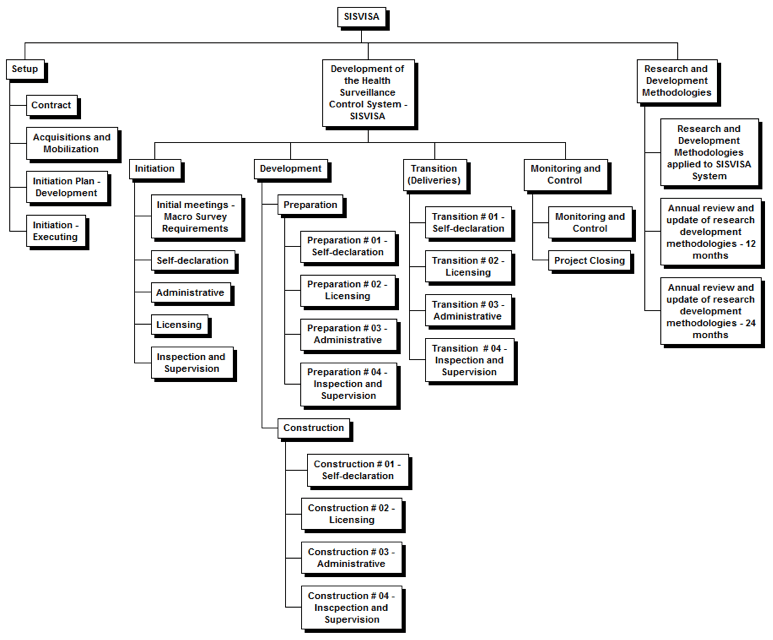
The researchers say the records seem to come from Brazil’s Health Surveillance Information System, called SISVISA. Even though the records looked linked to SISVISA, it is unclear if the database was owned and run by the organization or by another company.
This government platform helps health officials check sanitation. They inspect places like restaurants, hospitals, and pharmacies. It also helps with licenses and permits and monitors if health rules are followed.
After sending a warning to several agencies, public access was limited soon after and is not available now.
In a report from 2025, it was said that the SISVISA platform was created to fix problems in managing public health checks using technology. Public groups needed tools to make their work easier, cut costs, and work better. SISVISA was meant to help with running, managing, analyzing, and making decisions, improving the group’s ability to plan and connect tech with health goals.
Many government agencies worldwide switched to digital platforms years ago, but many are still changing to digital systems. This is why it is crucial to create apps and platforms with security as a priority. There are many risks when sharing documents and files that have PII and might not be meant for the public. These risks can be simple fraud, targeted phishing, or even identity theft.