 InfoSecBulletin Cybersecurity for mankind
The NSA advises iPhone and Android users to restart their devices weekly for better security against cyber threats. The NSA suggests in a document that regularly restarting devices is a simple and effective way to reduce the risk of cyberattacks. This advice is especially relevant due to the rising complexity of cyber threats on mobile devices.
NSA said restarting phones can disrupt malware and other malicious software. Malware can stay in a device’s memory, but restarting the device can clear the memory and stop the threat.
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

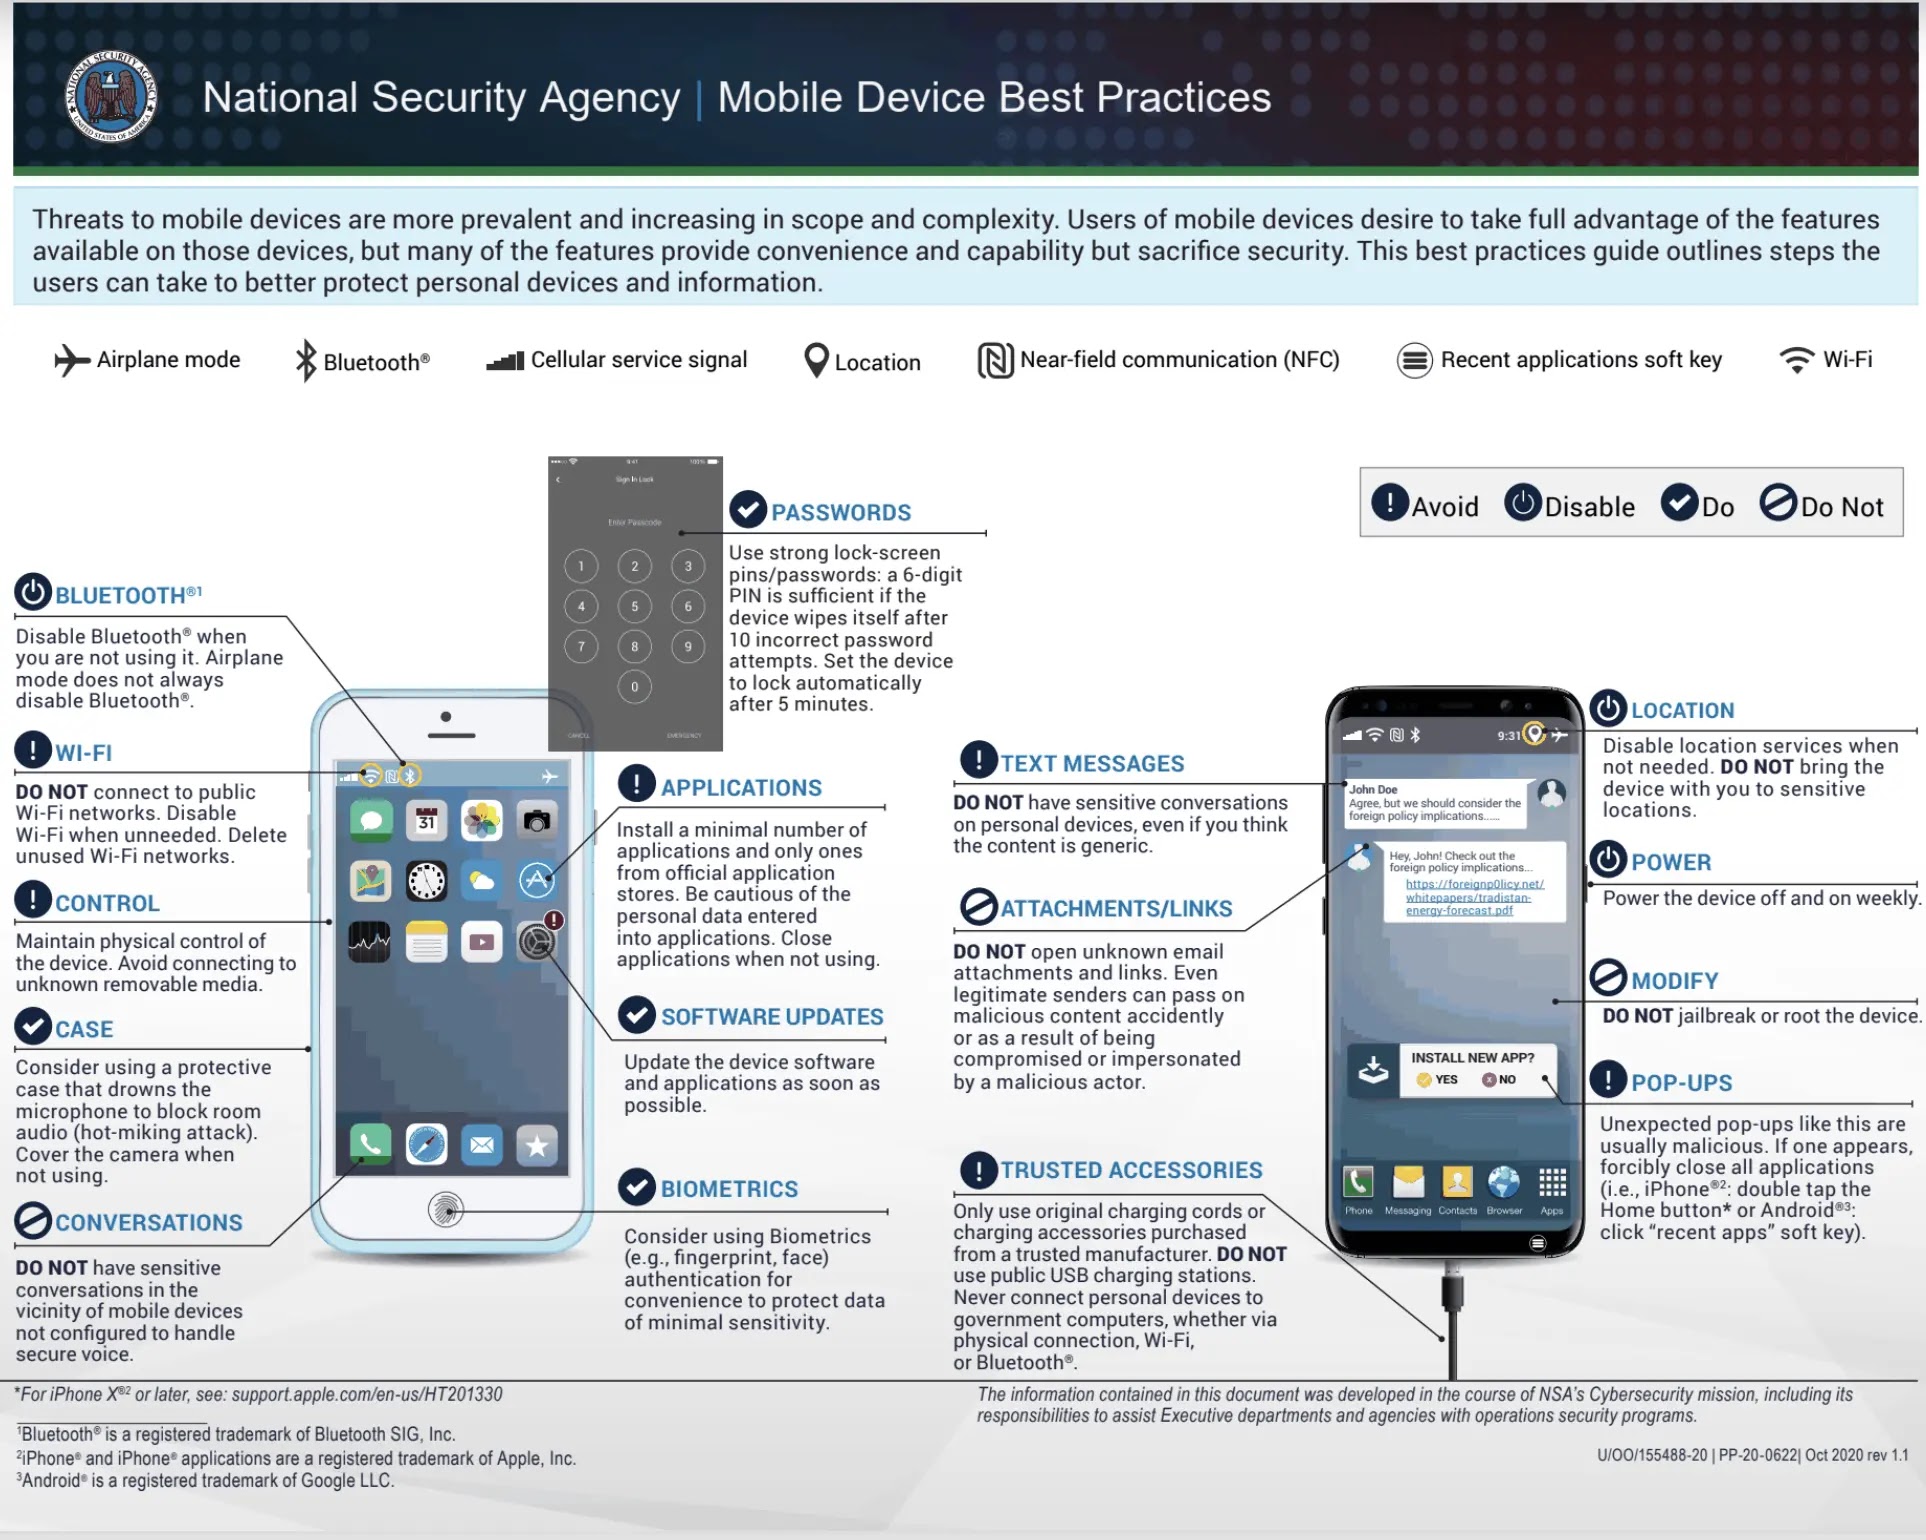
The NSA stated in the advisory, “Regularly restarting your mobile device can help ensure that any malicious code running in the background is terminated. This simple action can significantly reduce the risk of persistent malware infections.”
The advisory also emphasizes the importance of rebooting as a useful component of a comprehensive security strategy. The NSA suggests regular reboots, keeping the device updated, using strong passwords, and enabling multi-factor authentication.
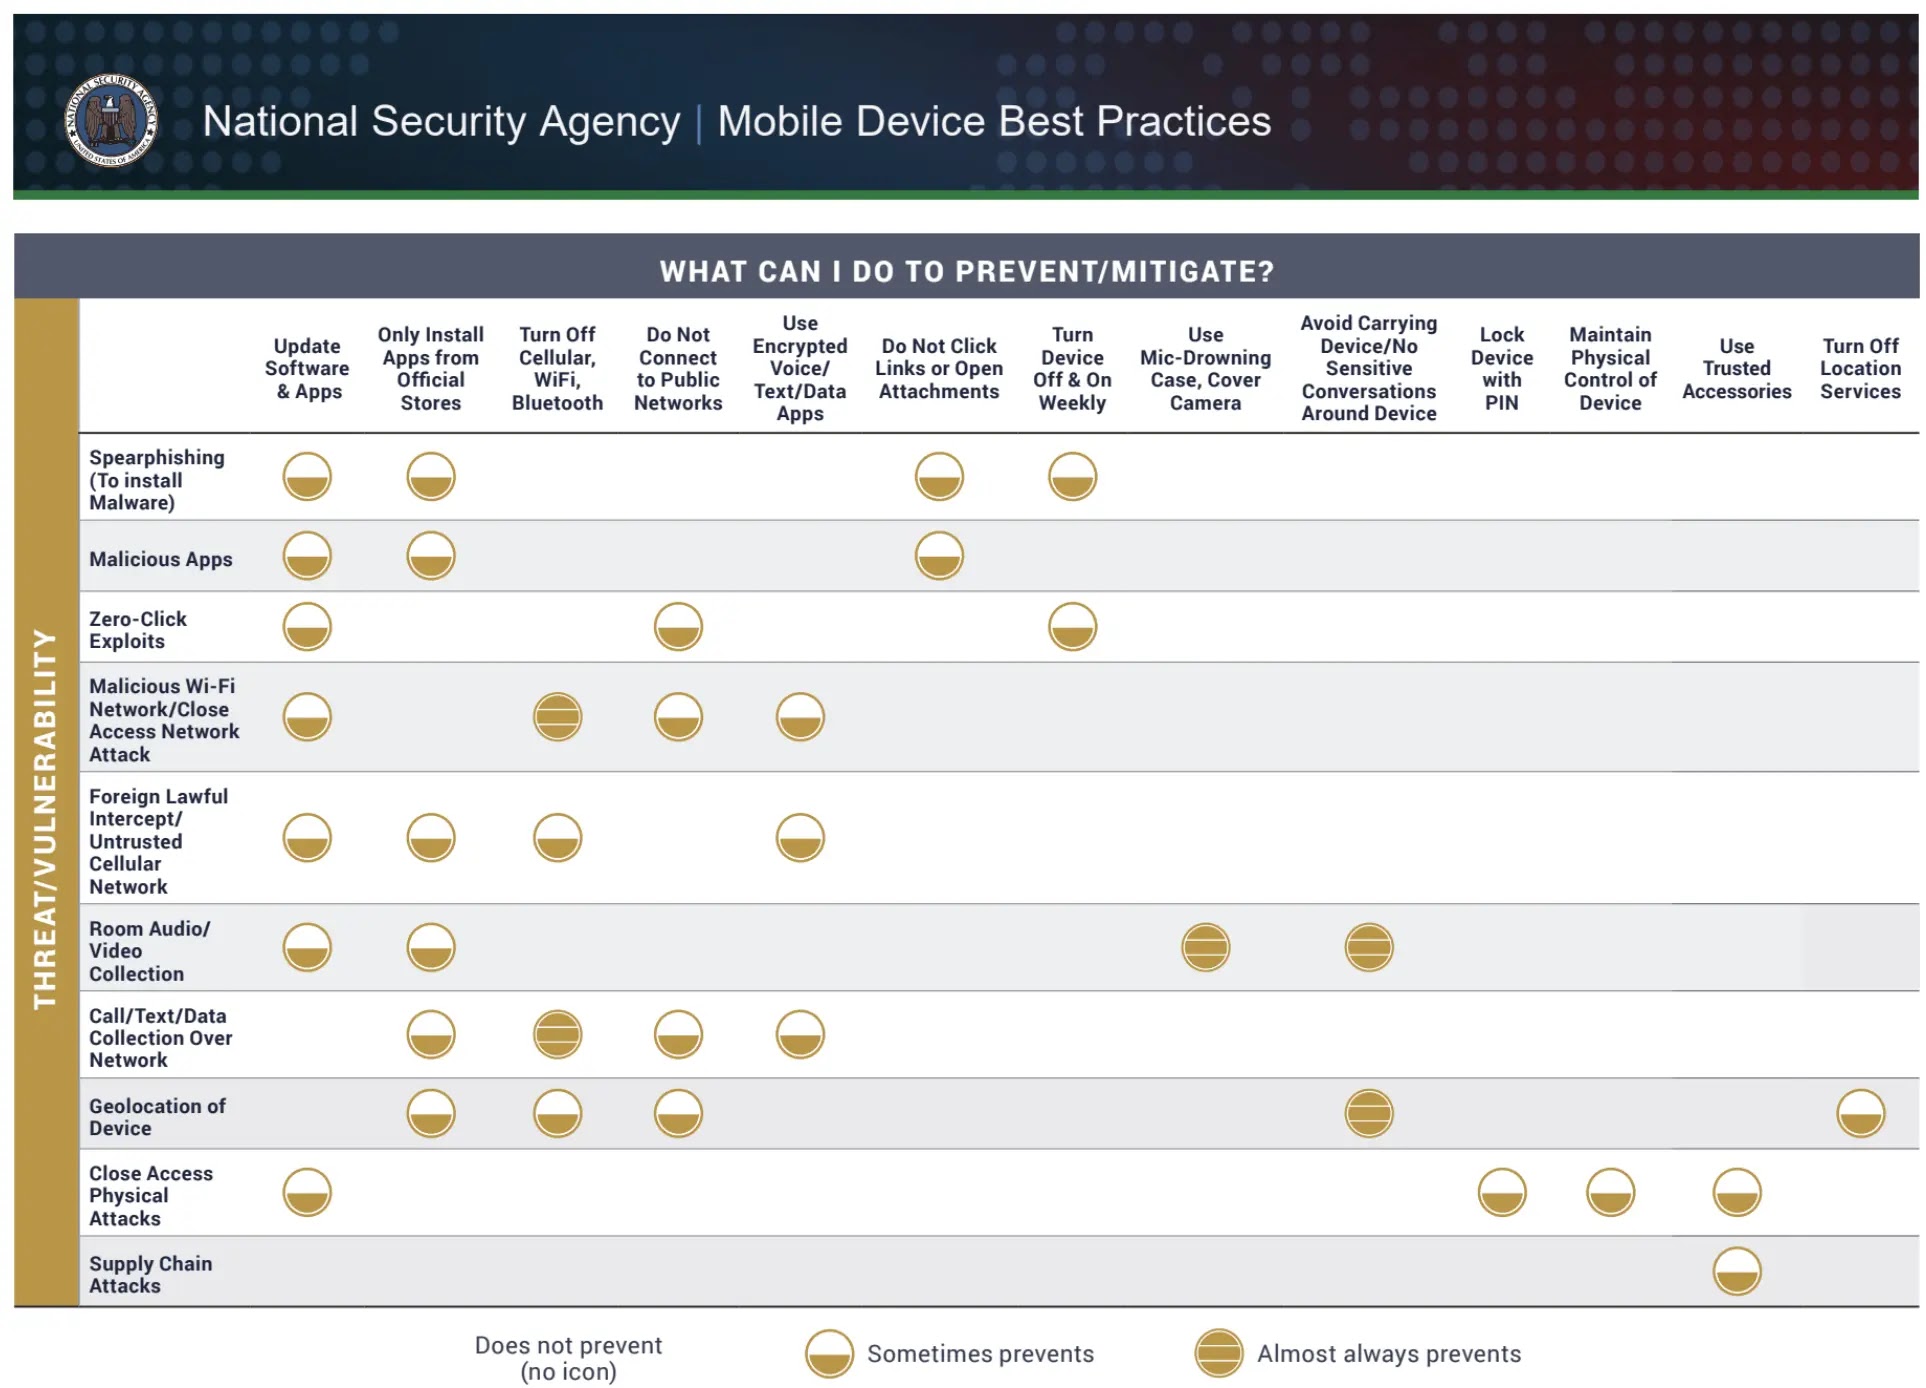
In addition to the weekly reboot recommendation, the NSA’s document outlines several other best practices for mobile device security:
Update Software Regularly:
Make sure the device’s system and installed apps are regularly updated with the latest security fixes and updates.
Use Strong Authentication:
Use two-step verification for added security.
Be Cautious with Public Wi-Fi:
Do not use public Wi-Fi networks for important transactions. If needed, use a VPN to make the connection secure.
Install Apps from Trusted Sources:
Only use official app stores.
Regularly Review App Permissions:
Regularly check and remove unnecessary or intrusive app permissions.
NSA warns that cyber threats to mobile devices are growing and becoming more advanced. Users need to prioritize strong security measures to protect against cybercriminals targeting mobile operating systems and apps.



