InfoSecBulletin Cybersecurity for mankind
Cybercriminals are using Telegram to advertise a new phishing kit called ‘V3B’. This kit is currently aimed at customers of 54 big financial institutions in Ireland, the Netherlands, Finland, Austria, Germany, France, Belgium, Greece, Luxembourg, and Italy.
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

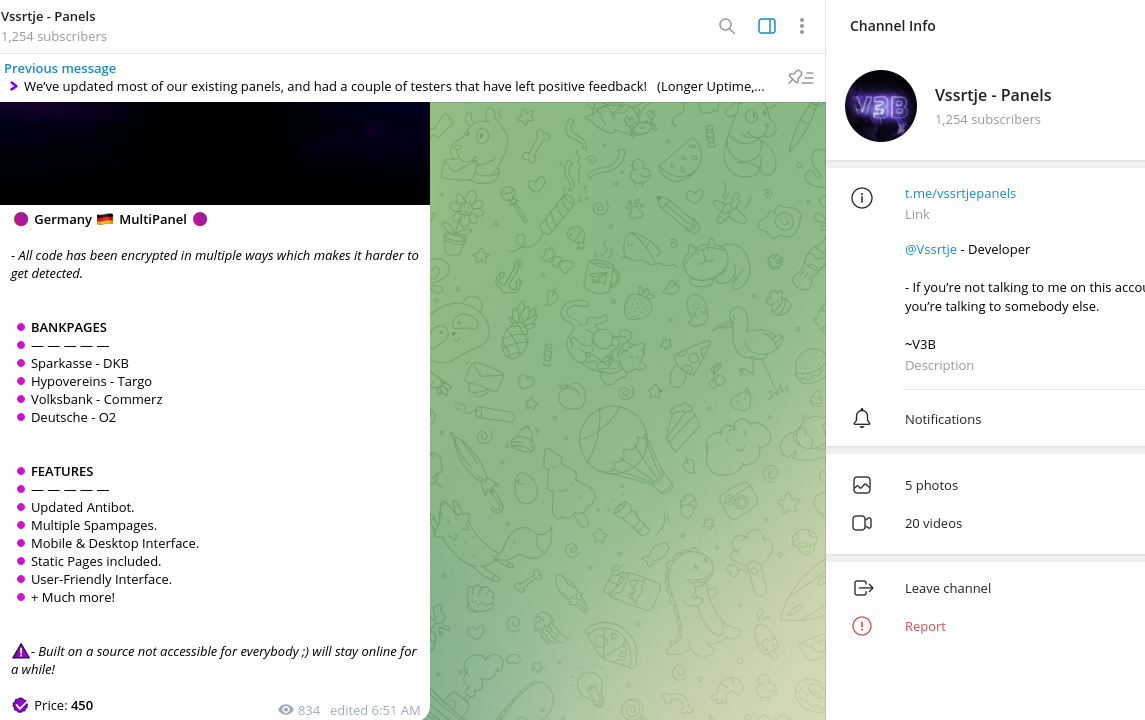
The phishing kit costs between $130 and $450 per month. It includes advanced hiding, language options, support for OTP/TAN/2FA, live chat with victims, and ways to avoid detection.
Resecurity researchers discovered V3B. Its Telegram channel has over 1,250 members, showing that the new phishing-as-a-service (PhaaS) platform is gaining popularity in cybercrime.
The threat actors have been mainly targeting banks in the European Union. They consider these banks a top priority. Phishing has caused European banking customers to lose a significant amount of money, estimated to be in the millions of euros. The bad actors have set up a network of money mules in European countries to handle stolen financial data and carry out illegal transactions.
Targeting Banks In European Union:
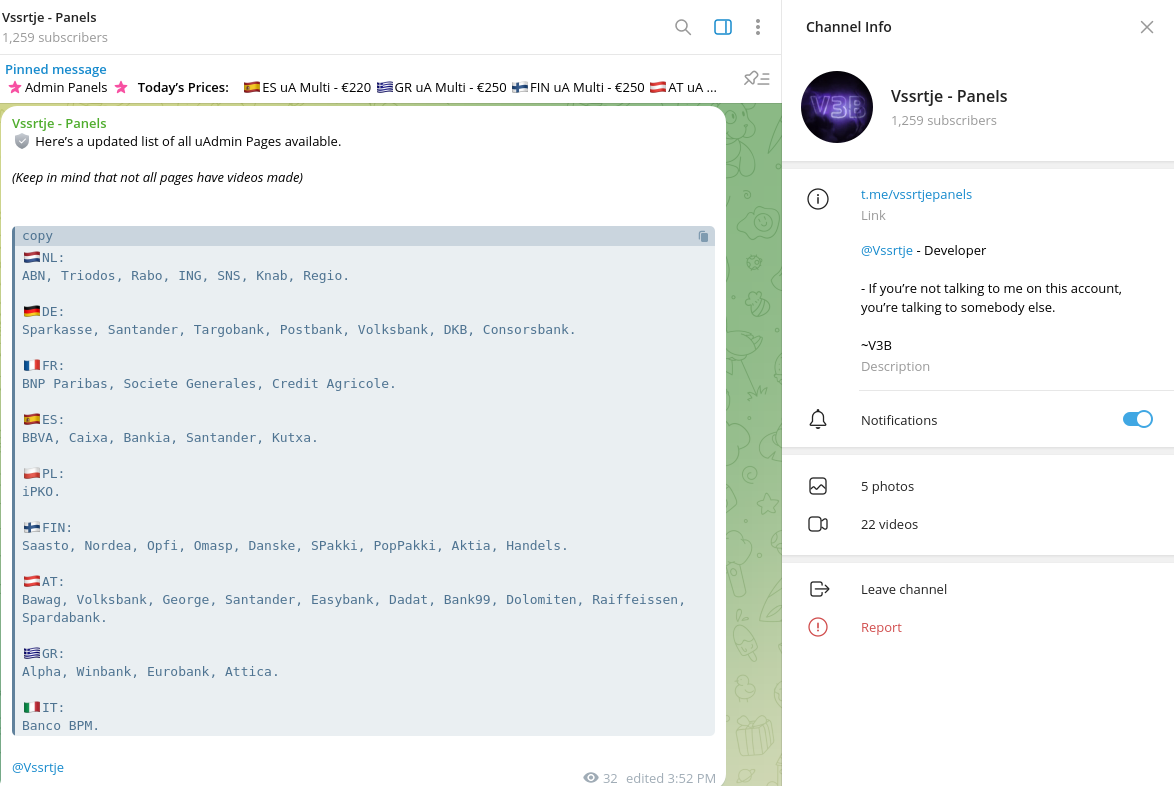
Resecurity has identified and reviewed multiple phishing kits targeting specific banks, including top financial institutions in the EU:
– Ireland
Allied Irish Banks
– Netherlands
ICS Cards
– Finland
Nordea, Danske, OP Bank, Aktia, HandelsBank
– Austria
Bawag, VolksBank, George, Santander, EasyBank, Volksbank, Dadat, Bank99, Dolomiten, Raiffeissen, Bawag, Spardabank
– Germany
Sparkasse, DKB, Hypovereins, Targo, Volksbank, Commerzbank, Deutsche Bank, O2
– France
Epargne, Agricole, Populaire, Bourso, Socgenerale, HSBC, Hello, BNP Paribas, ING Bank, AXA Bank, Credit Agricole, Societe Generale
– Belgium
Fintro, Argenta, BNP, KBC, AXA, Belfius, BPOST, ING
– Greece
AlphaBank
– Luxembourg
ING
– Italy
Banco BPM, Poste Italiane
The V3B phishing kit supports a wide range of financial institutions across the European Union, using customized templates to mimic online banking and e-commerce authentication processes.
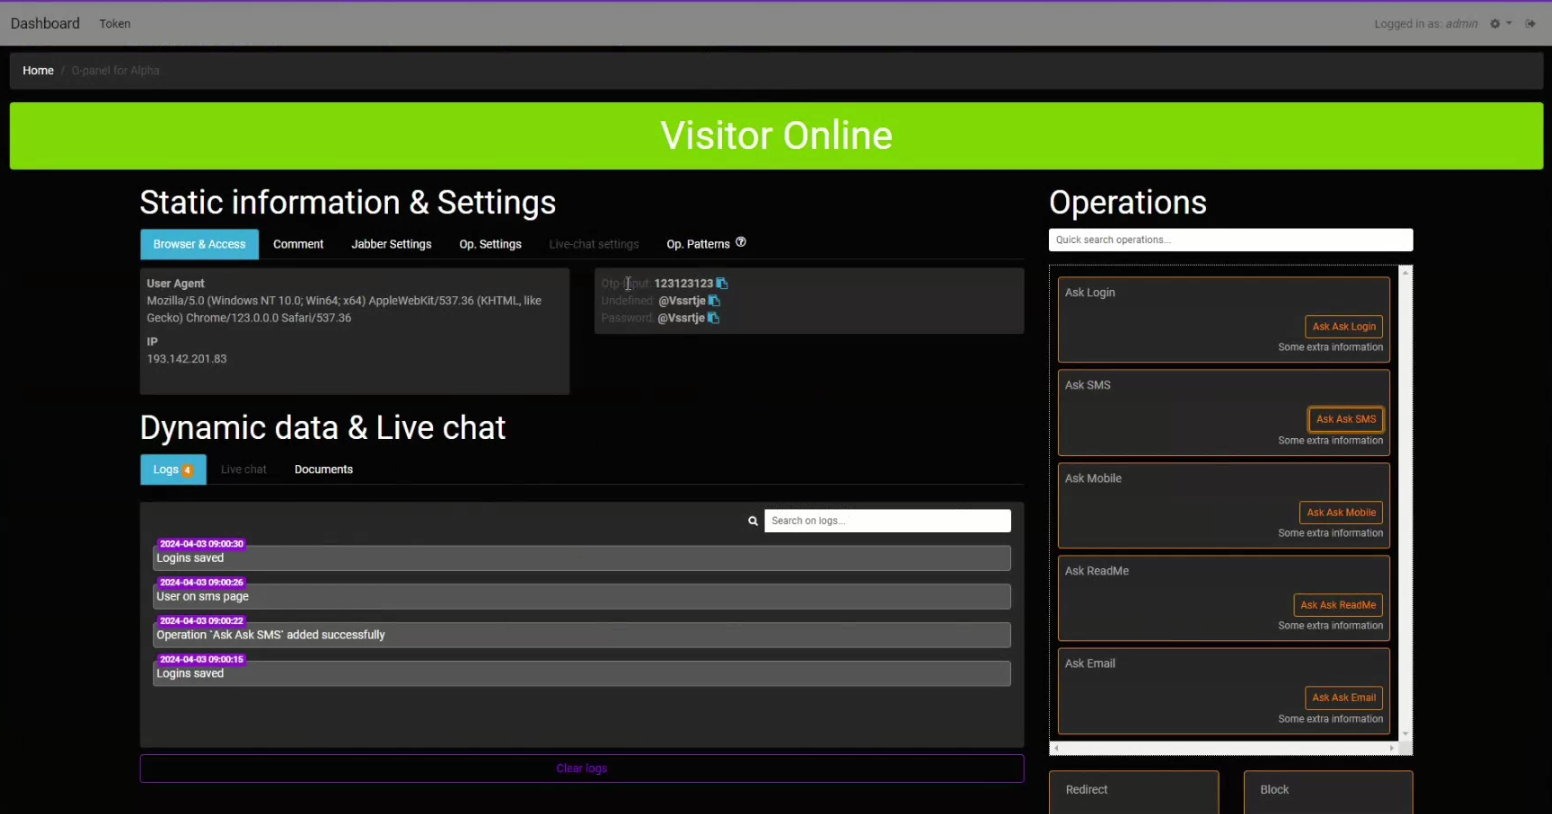
Key Features:
• Encrypted Code
The code for the live phishing kits is encrypted in multiple ways.
• Multi-Country Targeting
The kit targets multiple countries, including Ireland, the Netherlands, Finland, Austria, Germany, France, Belgium, Greece, Luxembourg, and Italy.
• Advanced Features
The kit has advanced features like updated tokens, anti-bot measures, mobile and desktop interfaces, live chat, and support for OTP/TAN/2FA including QR codes and PhotoTAN method.
• Persistence
The kit is built on a modified CMS with hidden scenarios, ensuring it will go unnoticed and stay online for long durations.
uPanel allows scammers to request OTP/tokens, deceiving people into entering their codes. The scammer can then use these codes to carry out transactions. for full report click here.