InfoSecBulletin Cybersecurity for mankind
KDDI Corporation, a Japanese telecom company, revealed a data breach. Hackers got into one of its email systems that five other internet providers use. The company found the incident on June 17 and quickly blocked the attacker and set up defense measures.
The investigation found that hackers took advantage of a weakness in a third-party software that KDDI Corporation used.
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks
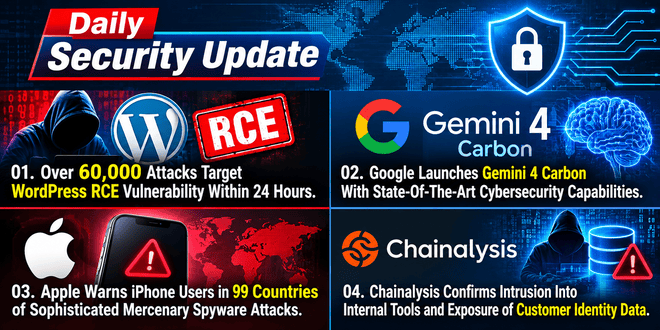
Daily Cyber security update for 31.10. 2026
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

“Although technical defensive measures have already been implemented for the system, there remains a possibility that customers’ email addresses and passwords were obtained by unauthorized third parties as a result of the incident,” KDDI warns.
Scale of exposure
KDDI is one of the biggest internet providers in Japan. It has 45,000 workers and makes about $32.4 billion each year. Since 2000, it has been a public company after IDO, DDI, and KDD merged. KDD was Japan’s old state-run international telecom provider.
The company says that the incident affected five internet service providers and their email systems:
STNet, Inc.
JCOM Co., Ltd.
Chubu Telecommunications C., Inc.
NIFTY Corporation
BIGLOBE Inc.
Although they are still looking into the incident and do not know how many accounts were affected, KDDI said it might have revealed the email addresses and passwords of about 14.22 million customers.
Another helpful point, as KDDI says, is that some passwords were kept in a hashed or encrypted way. This means they can’t easily be misused for account takeovers, even if they are leaked.
KDDI did not say what kind of encryption was used or how many accounts had passwords kept in plain text. KDDI says it has been reaching out to affected ISPs since June 17. It has also informed Japan’s Personal Information Protection Commission and the Ministry of Internal Affairs and Communications.
The company is working with ISPs to add more security steps to reduce the risks from this issue. Customers who might have been affected should change their email account passwords quickly. If two-factor authentication (2FA) is an option, it’s a good idea to set it up for more security.