InfoSecBulletin Cybersecurity for mankind
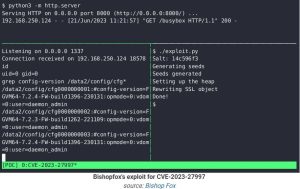
Hundreds of thousands of FortiGate firewalls are vulnerable to a critical security issue identified as CVE-2023-27997, almost a month after Fortinet released an update that addresses the problem.
The vulnerability is a remote code execution with a severity score of 9.8 out of 10 resulting from a heap-based buffer overflow problem in FortiOS, the operating system that connects all Fortinet networking components to integrate them in the vendor’s Security Fabric platform.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Fortinet addressed the vulnerability on June 11 before disclosing it publicly, by releasing FortiOS firmware versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, and 7.2.5.
ALSO READ:
Offensive security solutions company Bishop Fox reported on Friday that despite the calls to patch, more than 300,000 FortiGate firewall appliances are still vulnerable to attacks and reachable over the public internet.
Bishop Fox researchers used the Shodan search engine to find devices that responded in a way that indicated an exposed SSL VPN interface. They achieved this by searching for appliances that returned a specific HTTP response header.
They filtered the results to those that redirected to ‘/remote/login,’ a clear indication of an exposed SSL VPN interface.
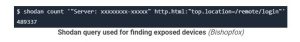
The query above showed 489,337 devices but not all of them were vulnerable to CVE-2023-27997, also referred to as Xortigate. Investigating further, the researchers discovered that 153,414 of the discovered appliances had been updated to a safe FortiOS version.
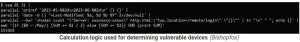
This means that roughly 335,900 of the FortiGate firewalls reachable over the web are vulnerable to attacks, a number that is significantly higher than the 250,000 recent estimation based on other, less accurate queries, Bishop Fox researchers say.
Another discovery Bishop Fox researchers made was that many of the exposed FortiGate devices did not receive an update for the past eight years, some of them running FortiOS 6, which reached end of support last year on September 29.
These devices are vulnerable to several critical-severity flaws that have proof-of-concept exploit code publicly available.