InfoSecBulletin Cybersecurity for mankind
Volkswagen Group has responded to claims from the ransomware group 8Base, which says it has stolen and leaked sensitive data from the company.
The German carmaker maintains that its core IT infrastructure remains unaffected; however, the company’s vague response leaves questions about the full scope of the incident and raises concerns about a possible third-party compromise.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

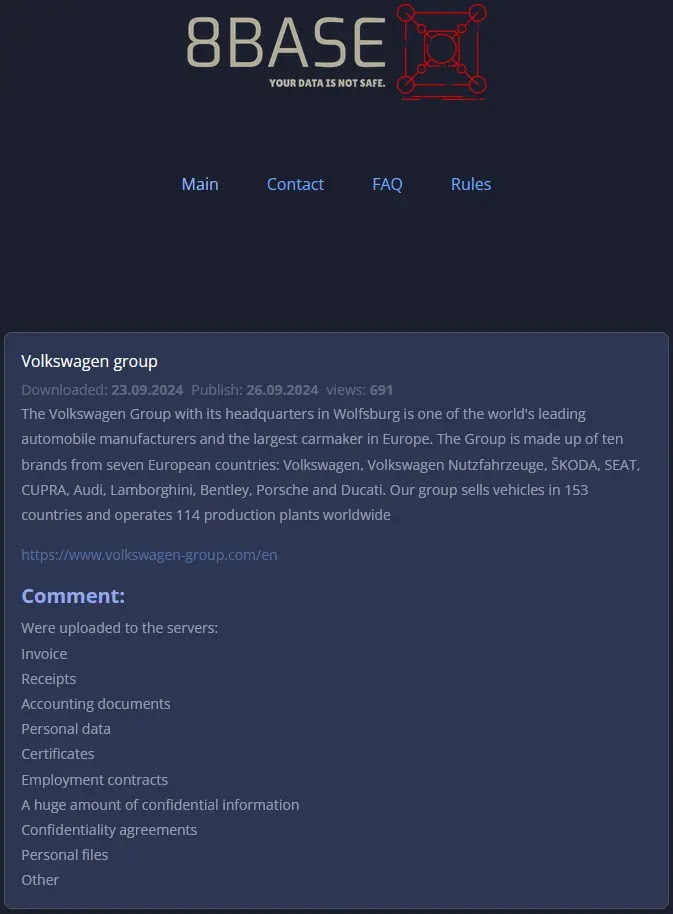
The ransomware group 8Base, active since early 2023, emerged in September 2024 claiming a significant breach at Volkswagen, one of the world’s largest automakers.
A group known for its Phobos ransomware and double-extortion tactics claimed to steal confidential files on September 23, 2024, and threatened to make them public by September 26.
8Base posted stolen data on its dark web site, including invoices, receipts, employee files, contracts, and confidentiality agreements, despite the deadline passing without any leaked samples.
This supposed collection may include financial documents and private details from Volkswagen’s global operations, spanning brands like Audi, Porsche, Bentley, Lamborghini, Skoda, SEAT, and Cupra.
Security experts note that 8Base operates more as a data extortion crew than a traditional encryptor, focusing on theft and threats to pressure victims into payment.
The group has attacked over 400 organizations since it started, usually gaining access through phishing or purchasing credentials from brokers.
Volkswagen’s Response:
Volkswagen’s spokesperson confirmed awareness of the “incident” but emphasized no impact on the company’s primary IT systems, hinting at a possible compromise through a supplier, partner, or subsidiary.
The automaker, headquartered in Wolfsburg, Germany, operates 153 production plants worldwide and employs hundreds of thousands, making any data exposure a high-stakes issue.
While no customer data breach has been reported, the inclusion of personal and financial details raises alarms under the EU’s GDPR, potentially leading to fines up to 4% of global revenue if substantiated.
Cybersecurity firms urge enhanced third-party risk management and monitoring, as such attacks often exploit weaker links in supply chains.
As investigations continue, the incident underscores the escalating threats to critical industries like automotive manufacturing.