 InfoSecBulletin Cybersecurity for mankind
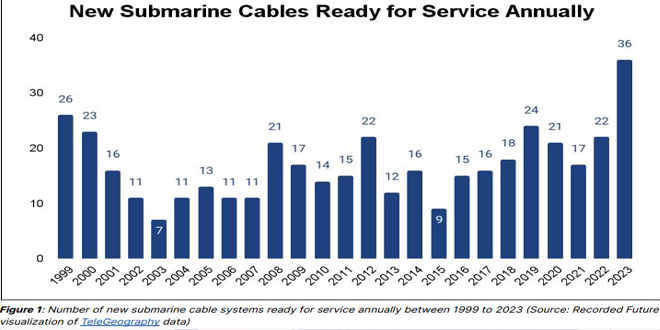
Insikt Group research examines the complex and dynamic risk environment of submarine cables, the information superhighways that underpin the global economy and facilitate worldwide telecommunications. The rapid expansion of the submarine cable network in the 21st century, driven by data demands, cloud computing, and the needs of hyperscalers like Amazon, Google, Meta, and Microsoft, must contend with converging geopolitical, physical, and cyber threats. State actors pose the greatest threat in terms of sabotage and spying, followed by non-state actors like hacktivists and ransomware groups, who pose a less capable and lower likelihood threat to the networks and operating systems that submarine cables rely upon. Accidental damage from ships and fishing vessels is more frequent but less impactful.
ALSO READ:
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Major geopolitical developments, specifically Russia’s conflict with Ukraine, China’s preparations for potential forceful unification with Taiwan, and the deterioration of US-China relations, are likely to fuel physical attacks and intelligence collection efforts against submarine cables. Notably, Russia has shown intent to map the submarine cable system in the Atlantic Ocean and North Sea, very likely for potential sabotage. The impact of these attacks will vary widely, ranging from intermittent traffic disruptions to widespread outages that take days or weeks to resolve, depending on the redundancy and resiliency of the affected network. State actors seeking an espionage edge will almost certainly target the entire submarine cable ecosystem for intelligence collection: landing station infrastructure, the submarine cables themselves, third-party providers, and the hardware and software that knits it all together.
Other major developments in the production, ownership, and operation of submarine cables have introduced new geopolitical challenges and created potential vulnerabilities. The rise of Chinese state-owned enterprises as cable owners, operators, and producers has elevated concerns over digital surveillance, while the expanding ownership stakes by hyperscalers has brought forward questions about market monopolies and digital sovereignty. Finally, the pursuit of expanded bandwidth capacity within the submarine cable industry has led to the adoption of advanced network management systems, which could be exploited for cyberattacks.
To read the entire analysis with endnotes, click here to download the report as a PDF.
Source: recordedfuture



