 InfoSecBulletin Cybersecurity for mankind
Days after the biggest crypto hack ever, another platform has experienced a major exploit. Infini Earn, a decentralized stablecoin bank, lost $49.5 million in USDC, making it one of the year’s biggest security breaches in DeFi.
Reportedly a compromised private key led to an attack that stole 11.4 million and 38 million USDC in two separate transactions.
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

The attacker quickly exchanged the stolen USDC for DAI and then purchased 17,696 ETH. They transferred the funds to a new wallet labeled “0xfcc8…6e49.”
Blockchain analysis indicates that the perpetrator might be someone connected to the initial contract development for Infini.
Reports indicate that the attacker kept admin access to the contract after finishing their work. Over 100 days later, they used Tornado Cash, a crypto mixing service, to hide their identity before carrying out the exploit.
Morpho MEVCapital’s USDC vault was breached, draining funds in two transactions. The hack is thought to have occurred due to unauthorized access to the platform’s private key.
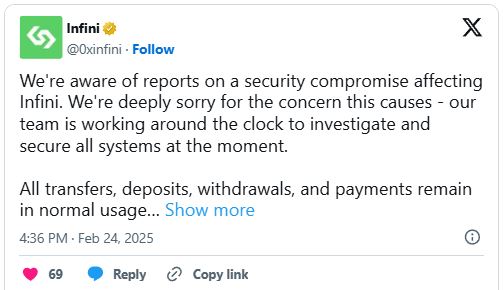
After the attack, Infini Earn’s founder, Christian Li, spoke about the incident on X.
Li accepted responsibility for the security lapse due to improper contract authority transfer, which allowed the exploit to occur.
“There is no problem with liquidity. Full compensation can be paid, and the funds are being traced. I know rebuilding trust will be a difficult process, but we won’t give up,” Li stated.
Li assured users that withdrawals are still available, but financial management operations have been suspended to minimize risks.
He stated that 70% of the stolen funds were from institutional investors and promised to cover the losses personally and resolve the matter privately.
Li announced plans to reinvest the remaining funds into Infini Vault by Monday to restore normal operations.



