 InfoSecBulletin Cybersecurity for mankind
In recent times, it has been observed by the security researchers at Kaspersky’s SecureList that the official Google Play store’s security has become increasingly vulnerable to the schemes of the threat actors.
These shady actors have exploited various loopholes to develop tools that can effectively Trojanize the existing Android applications, making them susceptible to exploitation.
Methodology
While here, the most shocking and alarming thing is that the threat actors are selling all these malicious wares for excessive sums of up to $20,000 on the dark web.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

A recent study conducted between 2019 and 2023 revealed a concerning trend in cybersecurity.
The research has uncovered a prosperous marketplace where buyers and sellers engage in the trading of:-
- App developer accounts
- Botnets
- Malicious Android applications
Certain wares, especially those extremely useful, are sometimes going for several thousands of dollars. As far as hiding malware and unwanted programs are concerned, the following categories are the most popular:
- Financial apps
- Cryptocurrency trackers
- Dating apps
- QR-code scanners
Malicious Services Offered
Various products, services, and deals are available on the dark web for customers with different needs and budgets, just like they are on legitimate online marketplaces.
Apart from this, threat actors have been observed buying a range of illicit products on the dark web, with developers’ Google Play accounts and source code for app development tools being among the most popular.
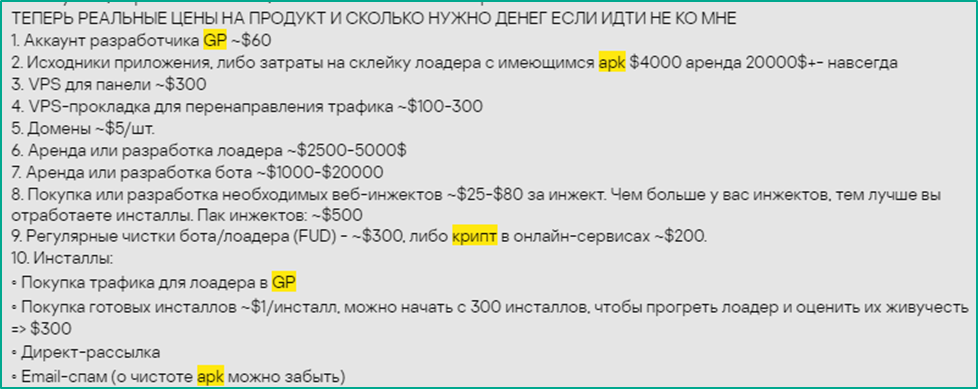
These accounts are often obtained through shady means, such as hacking or the use of stolen identities, enabling the threat actors to upload their malicious innovations to Google Play.
To be listed in Apple’s or Google’s app stores, software must undergo intensive testing before being uploaded.
Below we have mentioned all the major services offered in these marketplaces:-
- Google Play loaders
- Binding service
- Malware obfuscation
- Installations
- Other illicit services
Average Prices
During the research analysis, the security analysts discovered a wide range of price tags offered on the dark web for Google Play-related services.
For hassle-free trading and proceedings, they also accept payments through various methods. There are also some sellers who hold auctions as a means of selling their goods.
There are several options for providing services, including sharing the final profit, renting services, and selling them for a one-time fee.
Here below, we have mentioned all the average price tags:-
- A loader can cost between $2,000 and $20,000.
- A binding service usually costs about $50 to $100 or $65 per file.
- Obfuscation of 50 files may cost around $440.
- The average price tag for installation ranges between $0.25 to $1.
Recommendations
The following steps should be taken to stay protected against mobile threats:-
- Installing apps from unknown sources should not be enabled.
- Don’t grant an app permissions that it doesn’t need to perform its main functions without checking its permissions.
- Protect your device from malicious apps and adware with a reliable security solution.
- When an update becomes available for your operating system and important apps, immediately update them.
- Always use strong and unique passwords.
- Ensure to enable the 2FA wherever possible.



