 InfoSecBulletin Cybersecurity for mankind
Palo Alto Networks fixed a vulnerability that could let attackers to disable firewall protections in DoS attacks. CVE-2026-0227 is a security issue impacting next-gen firewalls using PAN-OS 10.1 or later and Prisma Access configurations when the GlobalProtect gateway or portal is active.
The cybersecurity company reports that most cloud-based Prisma Access instances are already patched, and the remaining ones are set for an upgrade.
Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

“A vulnerability in Palo Alto Networks PAN-OS software enables an unauthenticated attacker to cause a denial of service (DoS) to the firewall. Repeated attempts to trigger this issue results in the firewall entering into maintenance mode,” Palo Alto Networks warns.
“We have successfully completed the Prisma Access upgrade for most of the customers, with the exception of few in progress due to conflicting upgrade schedules. Remaining customers are being promptly scheduled for an upgrade through our standard upgrade process.”
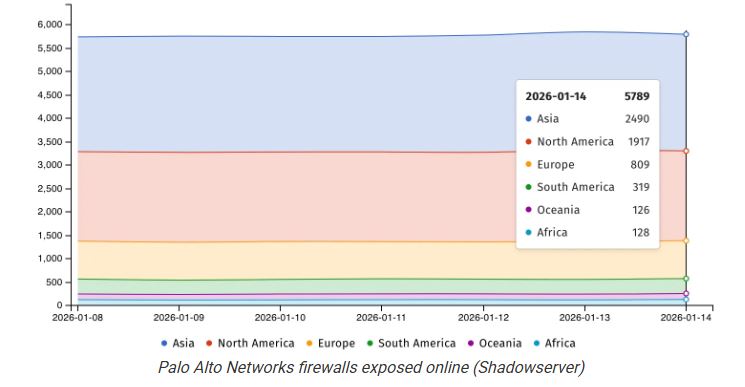
Internet security watchdog Shadowserver currently tracks nearly 6,000 Palo Alto Networks firewalls exposed online, though there is no information on how many have vulnerable configurations or have already been patched.
Palo Alto Networks has issued security updates for all affected versions. Admins should upgrade to the latest release to protect their systems from attacks.
| Version | Minor Version | Suggested Solution |
|---|---|---|
| Cloud NGFW All | No action needed. | |
| PAN-OS 12.1 | 12.1.0 through 12.1.3 | Upgrade to 12.1.4 or later. |
| PAN-OS 11.2 | 11.2.8 through 11.2.10 | Upgrade to 11.2.10-h2 or later. |
| 11.2.5 through 11.2.7 | Upgrade to 11.2.7-h8 or 11.2.10-h2 or later. | |
| 11.2.0 through 11.2.4 | Upgrade to 11.2.4-h15 or 11.2.10-h2 or later. | |
| PAN-OS 11.1 | 11.1.11 through 11.1.12 | Upgrade to 11.1.13 or later. |
| 11.1.7 through 11.1.10 | Upgrade to 11.1.10-h9 or 11.1.13 later. | |
| 11.1.5 through 11.1.6 | Upgrade to 11.1.6-h23 or 11.1.13 or later. | |
| 11.1.0 through 11.1.4 | Upgrade to 11.1.4-h27 or 11.1.13 or later. | |
| PAN-OS 10.2 | 10.2.17 through 10.2.18 | Upgrade to 10.2.18-h1 or later. |
| 10.2.14 through 10.2.16 | Upgrade to 10.2.16-h6 or 10.2.18-h1 or later. | |
| 10.2.11 through 10.2.13 | Upgrade to 10.2.13-h18 or 10.2.18-h1 or later. | |
| 10.2.8 through 10.2.10 | Upgrade to 10.2.10-h30 or 10.2.18-h1 or later. | |
| 10.2.0 through 10.2.7 | Upgrade to 10.2.7-h32 or 10.2.18-h1 or later. | |
| Unsupported PAN-OS | Upgrade to a supported fixed version. | |
| Prisma Access 11.2 | 11.2 through | Upgrade to 11.2.7-h8 or later. |
| Prisma Access 10.2 | 10.2 through | Upgrade to 10.2.10-h29 or later. |
The company announced on Wednesday that it has not found evidence of the vulnerability being exploited in attacks.



