 InfoSecBulletin Cybersecurity for mankind
Almost 22,000 Microsoft Exchange servers are online and still vulnerable to a flaw that lets attackers access all user mailboxes. Tracked as CVE-2026-62911 and reported by Orange Tsai from DEVCORE Research Team, this security flaw impacts Exchange Server 2016, Exchange Server 2019, and Exchange Server Subscription Edition (SE) software.
“Authentication bypass by capture-replay in Microsoft Exchange Server allows an authorized attacker to elevate privileges over a network,” Microsoft said when it patched the vulnerability during the August 2026 Patch Tuesday. “The attacker would be able to take over the mailboxes of all Exchange users, attackers can send emails, read emails, download attachments.”
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

Microsoft has not updated the CVE-2026-62911 advisory to confirm it yet, but the Netherlands National Cyber Security Centre (NCSC-NL) said last week that code to exploit the flaw is already online.
“Microsoft has made updates available to address the vulnerabilities. Install these updates as soon as possible,” NCSC-NL noted. “Exchange Server 2016 and 2019 only receive security updates via the Extended Security Updates Program (ESU). Are you using one of these versions? If so, ensure that the server is accessible only internally and replace it if possible.”
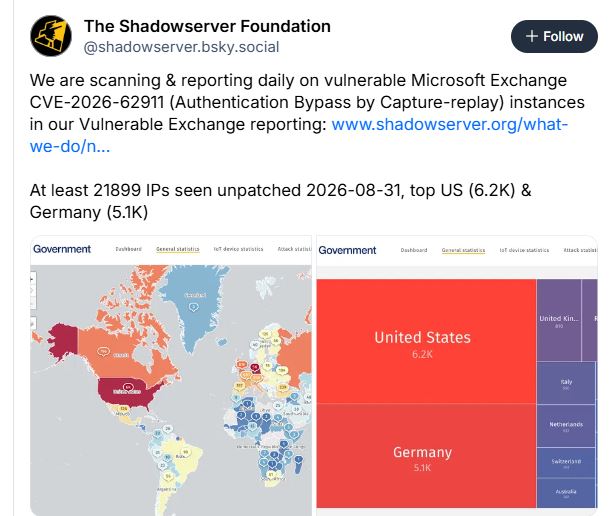
On Tuesday, Shadowserver found 21,899 IP addresses with Microsoft Exchange Server online that need updates. Most of them are in the United States (6,200) and Germany (5,100).
Germany’s Federal Office for Information Security (BSI) warned on Friday (as first spotted by Heise) that about 85% of all on-premises Exchange servers in Germany are still at risk from this problem.
CVE-2026-62911 has not been reported as used in real attacks yet, but Microsoft fixed another problem in Exchange Server (CVE-2026-42897) in June. This flaw was used in XSS attacks against Outlook Web Access users. CISA added CVE-2026-42897 to its list of known flaws on May 15 and told U.S. government agencies to fix their servers in two weeks.
Since November 2021, CISA has added 20 problems with Microsoft Exchange Server to its list of security issues being used in attacks. 14 of these are linked to ransomware attacks.
In October, Microsoft said that Exchange 2016 and 2019 are no longer supported. CISA and the NSA then shared advice on making Exchange servers more secure against attacks.
Two months ago, Microsoft told customers that security updates for Exchange 2016 and Exchange 2019 will end in October 2026 under the Extended Security Update (ESU) program.



