InfoSecBulletin Cybersecurity for mankind
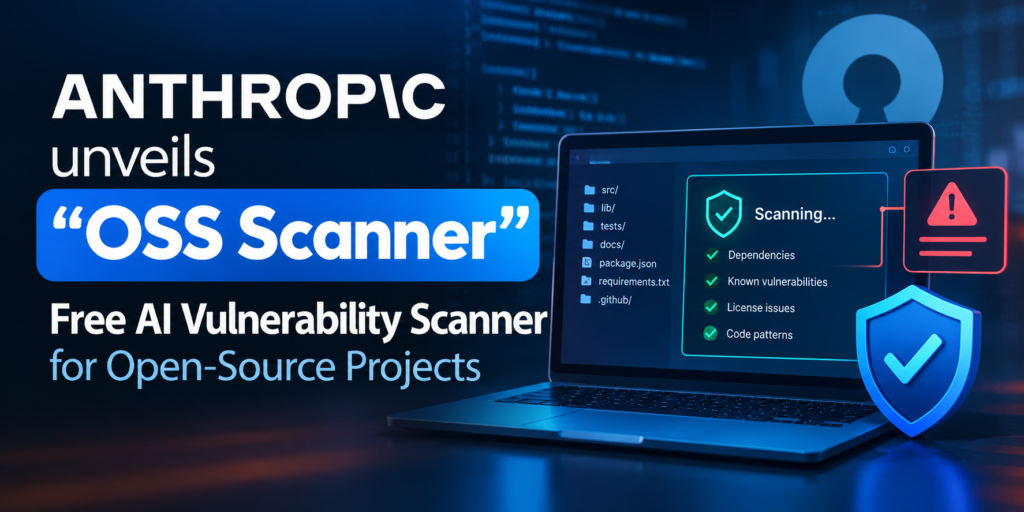
Anthropic unveiled OSS Scanner on Thursday as an opt-in vulnerability scanner designed to enhance security within the open-source ecosystem through artificial intelligence (AI).
“It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

Anthropic also noted that the outputs of the scanner will be fully model-generated and do not require human review or triage, thereby facilitating faster and more frequent scanning.
The company pointed out that it expects to use a set of criteria similar to Google’s OSS-Fuzz to pick projects, while emphasizing that the process may evolve over time. Project maintainers are advised to provide a short description explaining the importance of their project in cases where “it is not already self-evident.”
Core maintainers of a project can enroll by opening a pull request on the OSS Scanner’s GitHub repository along with a YAML configuration file that provides the following information –
Link to the git repository that should be cloned
Email address of the primary contact
A repository-relative path to the Dockerfile that sets up the environment, pre-installs all dependencies and builds the project so to help an offline agent conduct its security audit
“The Dockerfile configures the environment that the project will run in and installs all dependencies so that the agent can perform its security audit without any internet access,” Anthropic said. “We recommend verifying that the test cases pass inside of the built container.”
Other optional details that can be added to the YAML file are below –
Additional email addresses that are to be CC’ed on all reports
Project home page
GPG public key to encrypt report emails
A repository-relative path to a threat model file (“threat_model.md”) that spells out what code should be tested, vulnerability classification, or report formats.
Opt out of receiving bug reports by setting “disabled: true”
As of writing, a total of 116 pull requests have been submitted. Unlike other vulnerability reporting programs, Anthropic said it does not intend to impose a 90-day disclosure period on the findings, given the risk that they may contain false positives.
“If we later validate one of these reports manually through our existing CVD program, we may disclose it under our CVD policy starting 90 days from when you are notified that a human has validated this report,” it added. “As we gain greater confidence in OSS Scanner’s performance, we may in the future impose a disclosure period on some high-severity vulnerability reports.”
The AI company said it has identified more than 29,000 candidate vulnerabilities in some of the world’s most important software projects, out of which a little more than 6,000 flaws have been reported to maintainers. These have resulted in 584 advisories as of October 2, 2026.
The development comes as Anthropic also unveiled the Critical Infrastructure Defense Program to safeguard critical infrastructure and open-source software as part of its Cyber Mission.
With AI increasingly equipping bad actors to discover and exploit vulnerabilities, automate various stages of cyber operations, and conduct attacks faster and at scale, the idea behind the initiative is to arm defenders with the right tools to combat the threat, accelerate fixes, and explore new secure architectures and coding practices.
“Our forecast is that in two years, AI will favor defense: it will be easier to catch bugs before they ship, write fundamentally secure software from scratch, and actively defend systems with models,” Anthropic said.