 InfoSecBulletin Cybersecurity for mankind

92% of Microsoft Exchange servers in Germany are outdated and won’t get any more security updates, as warned by the German Federal Office for Information Security (BSI). The BSI in Germany reports about 33,000 on-premise Exchange servers with publicly accessible Outlook Web Access.
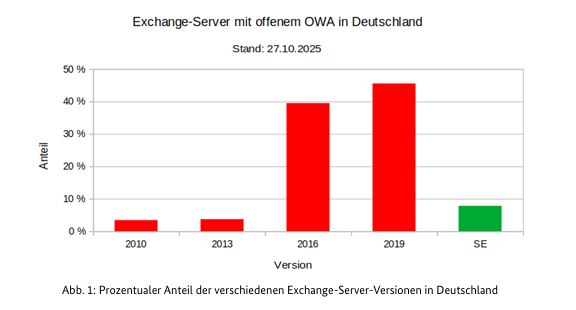
About 30,360 servers are running Exchange 2019 or older, while the supported Exchange Server Subscription Edition (SE) is found on over 2,500 systems.
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Over 45% of Exchange servers in the country are running version 2019, while around 40% are running version 2016. It’s just a matter of time before critical vulnerabilities are discovered in the unsupported software.
“In addition to thousands of companies, a large number of hospitals and doctors’ offices, schools and universities, social services, law and tax firms, public utilities, and municipal administrations are also affected,” the translation of the BSI alert reads.
The watchdog warns that many organizations have flat networks with poor segmentation and security. A compromised Exchange server can lead to a full network breach, resulting in data theft, ransomware attacks, and long production outages.
“Should a critical vulnerability in Microsoft Exchange become known in the near future – as has happened several times in recent years – it cannot be patched with a security update. The affected Exchange servers may then need to be taken offline immediately to avoid compromise. The consequence would be a massive disruption of the communication capabilities of the affected organizations,” BSI warns.
BSI recognizes that Microsoft’s Extended Security Update Program offers extra critical updates for a fee, but it’s only valid for six months (until April 14th, 2026) and requires more funding while only delaying necessary system upgrades.
BSI is urging Exchange server admins to “immediately upgrade to version SE or migrate to an alternative solution.”
The watchdog advises against exposing Exchange Server services, like web access, to the internet. Organizations should use a VPN for secure access or restrict it to trusted IP addresses.



